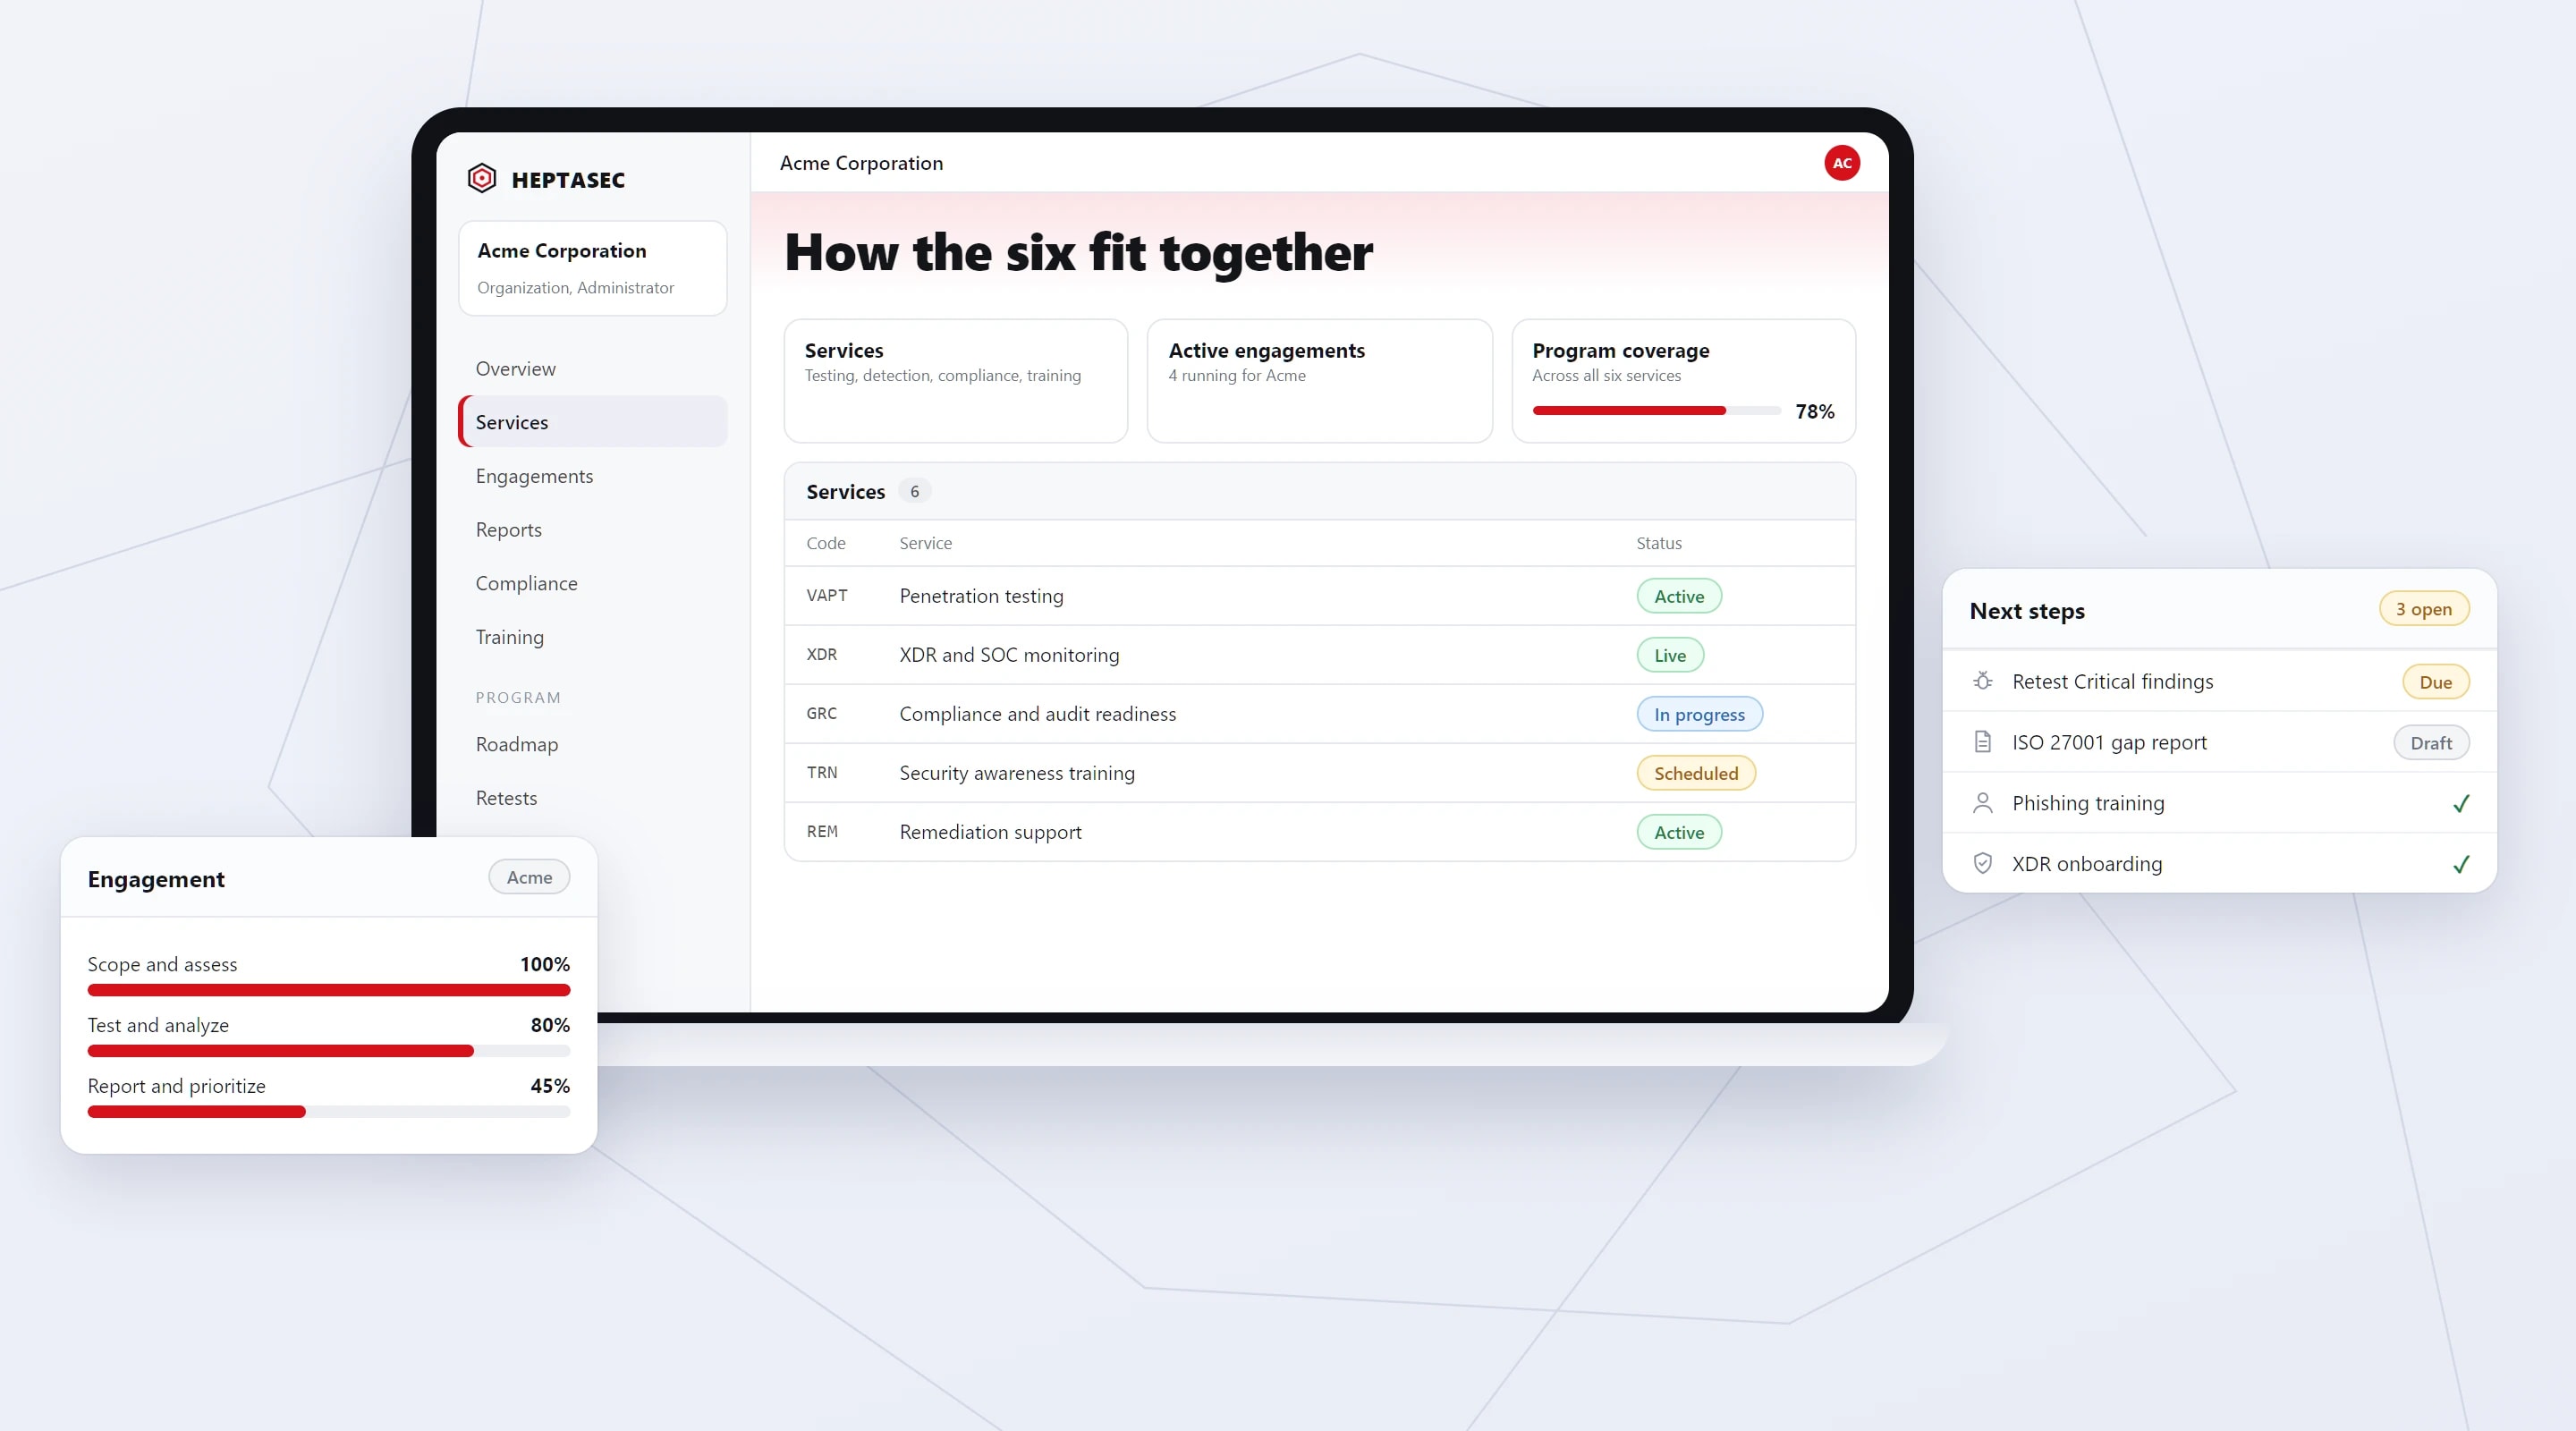
Six services. One security program.
Each service is designed to work independently, or as part of a continuous program.
01XDRFlagship
Unified Threat Detection & Response
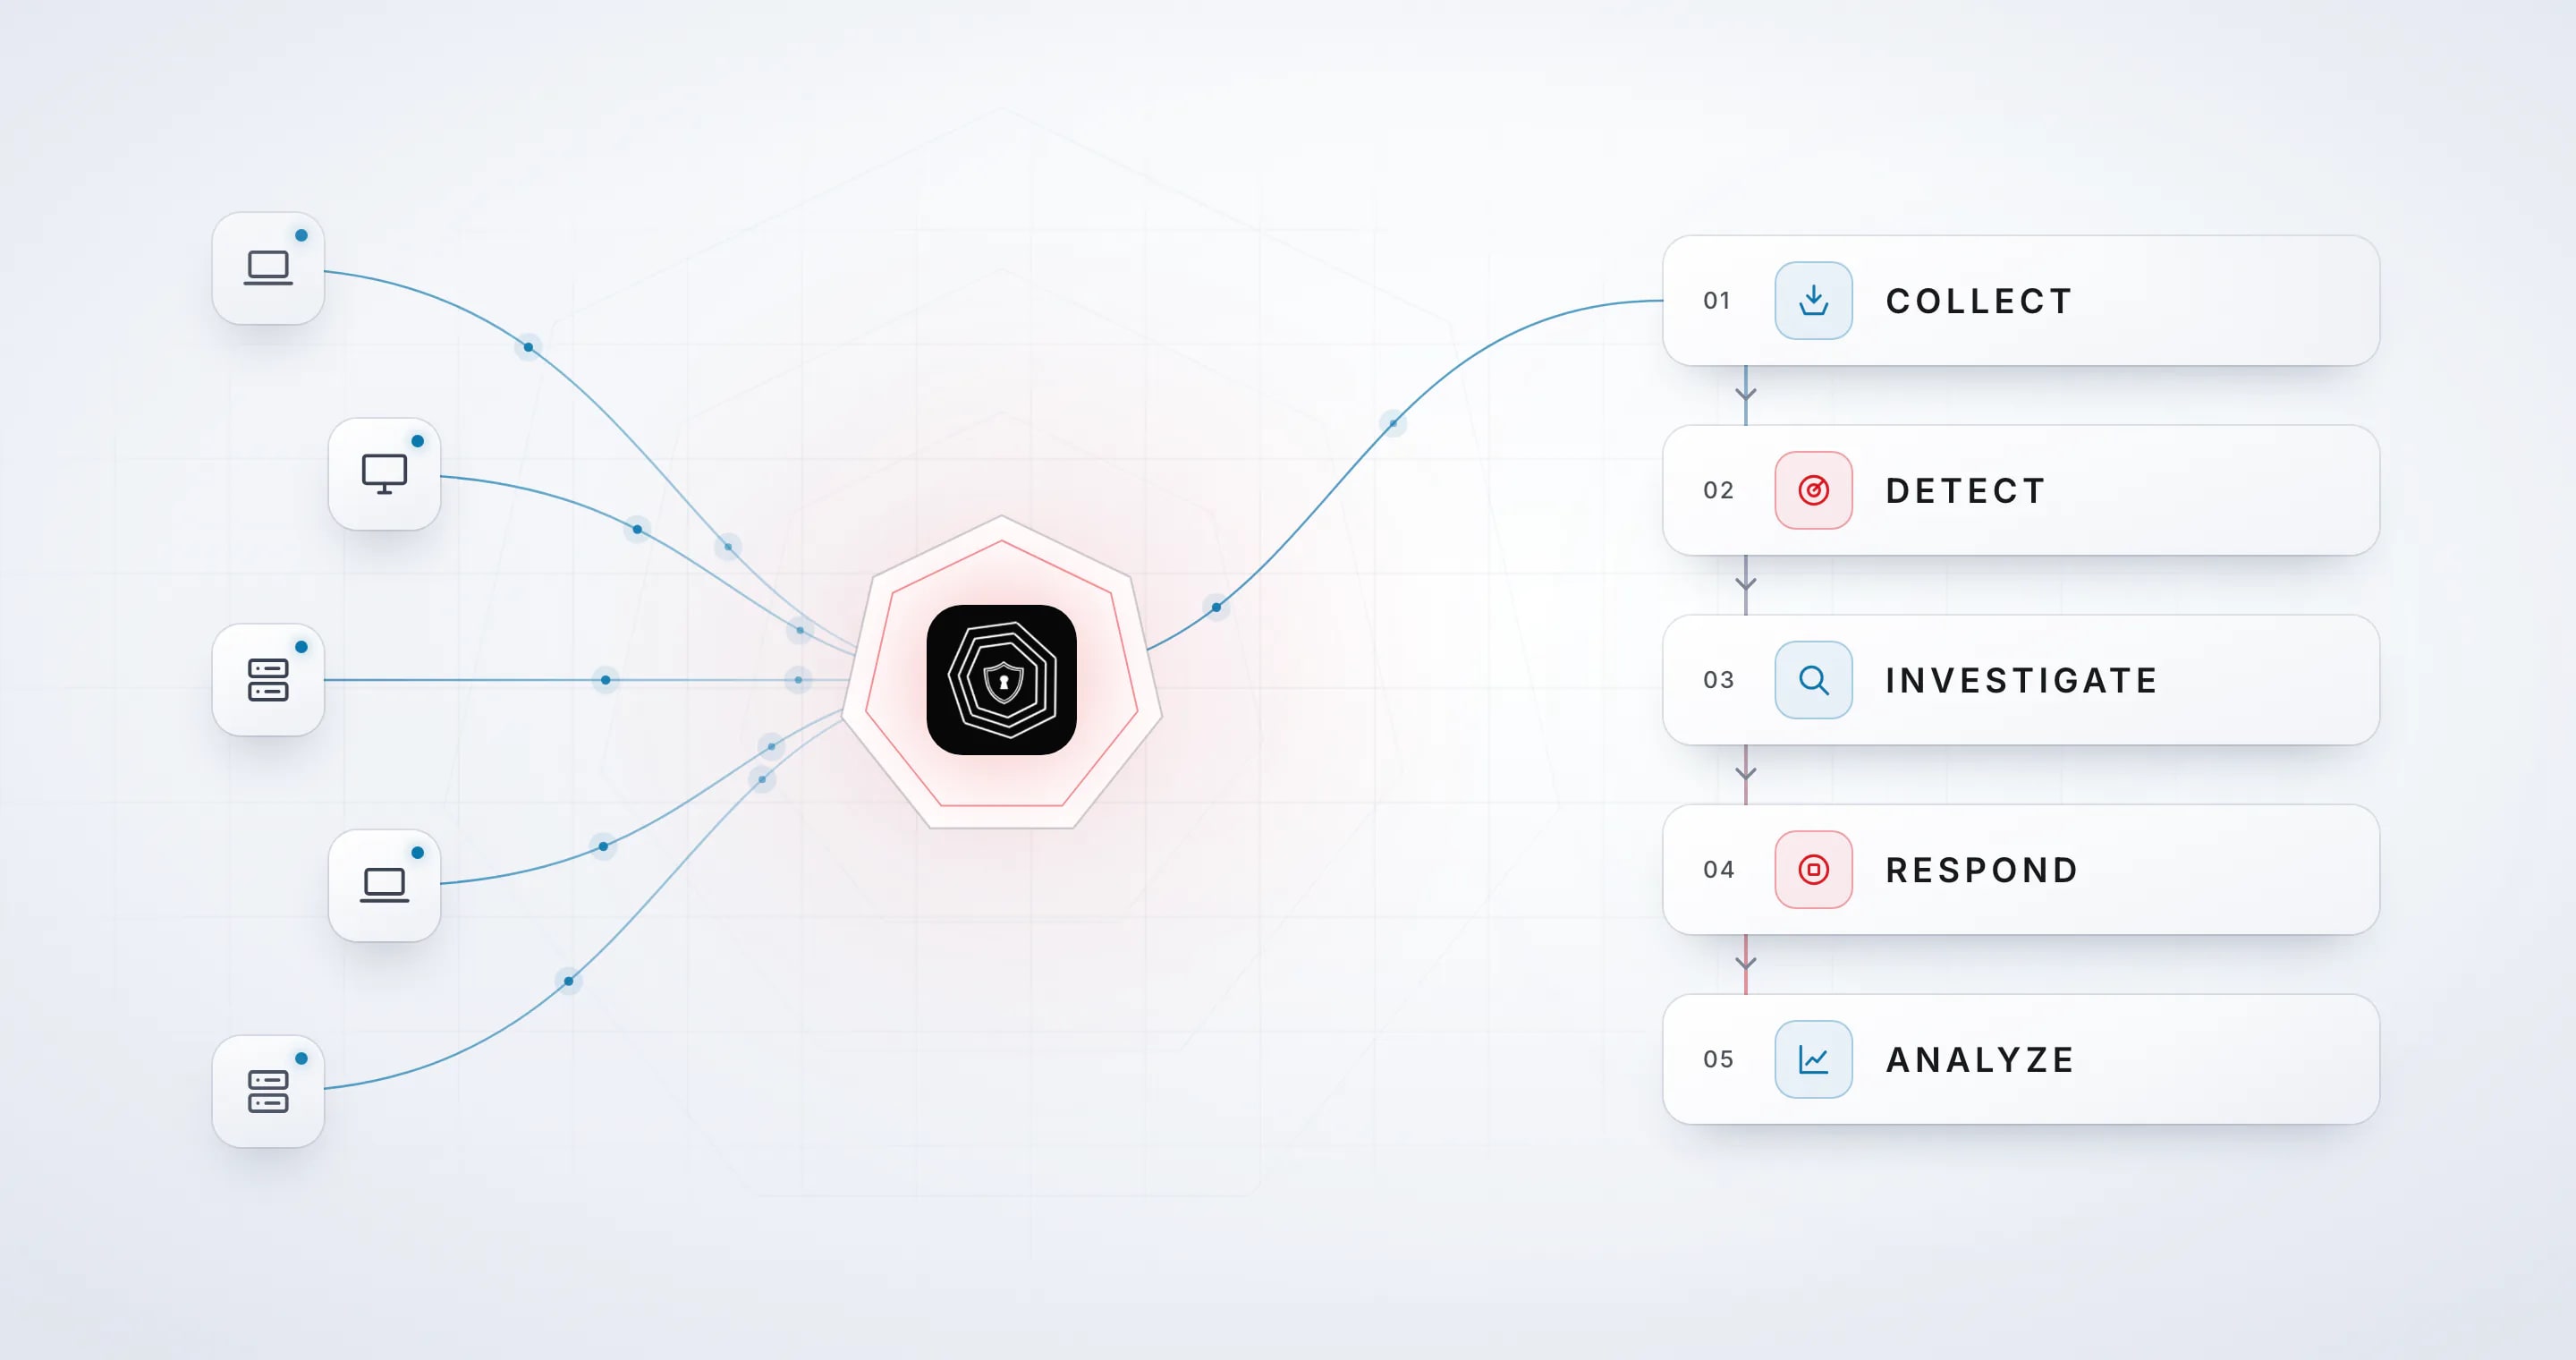
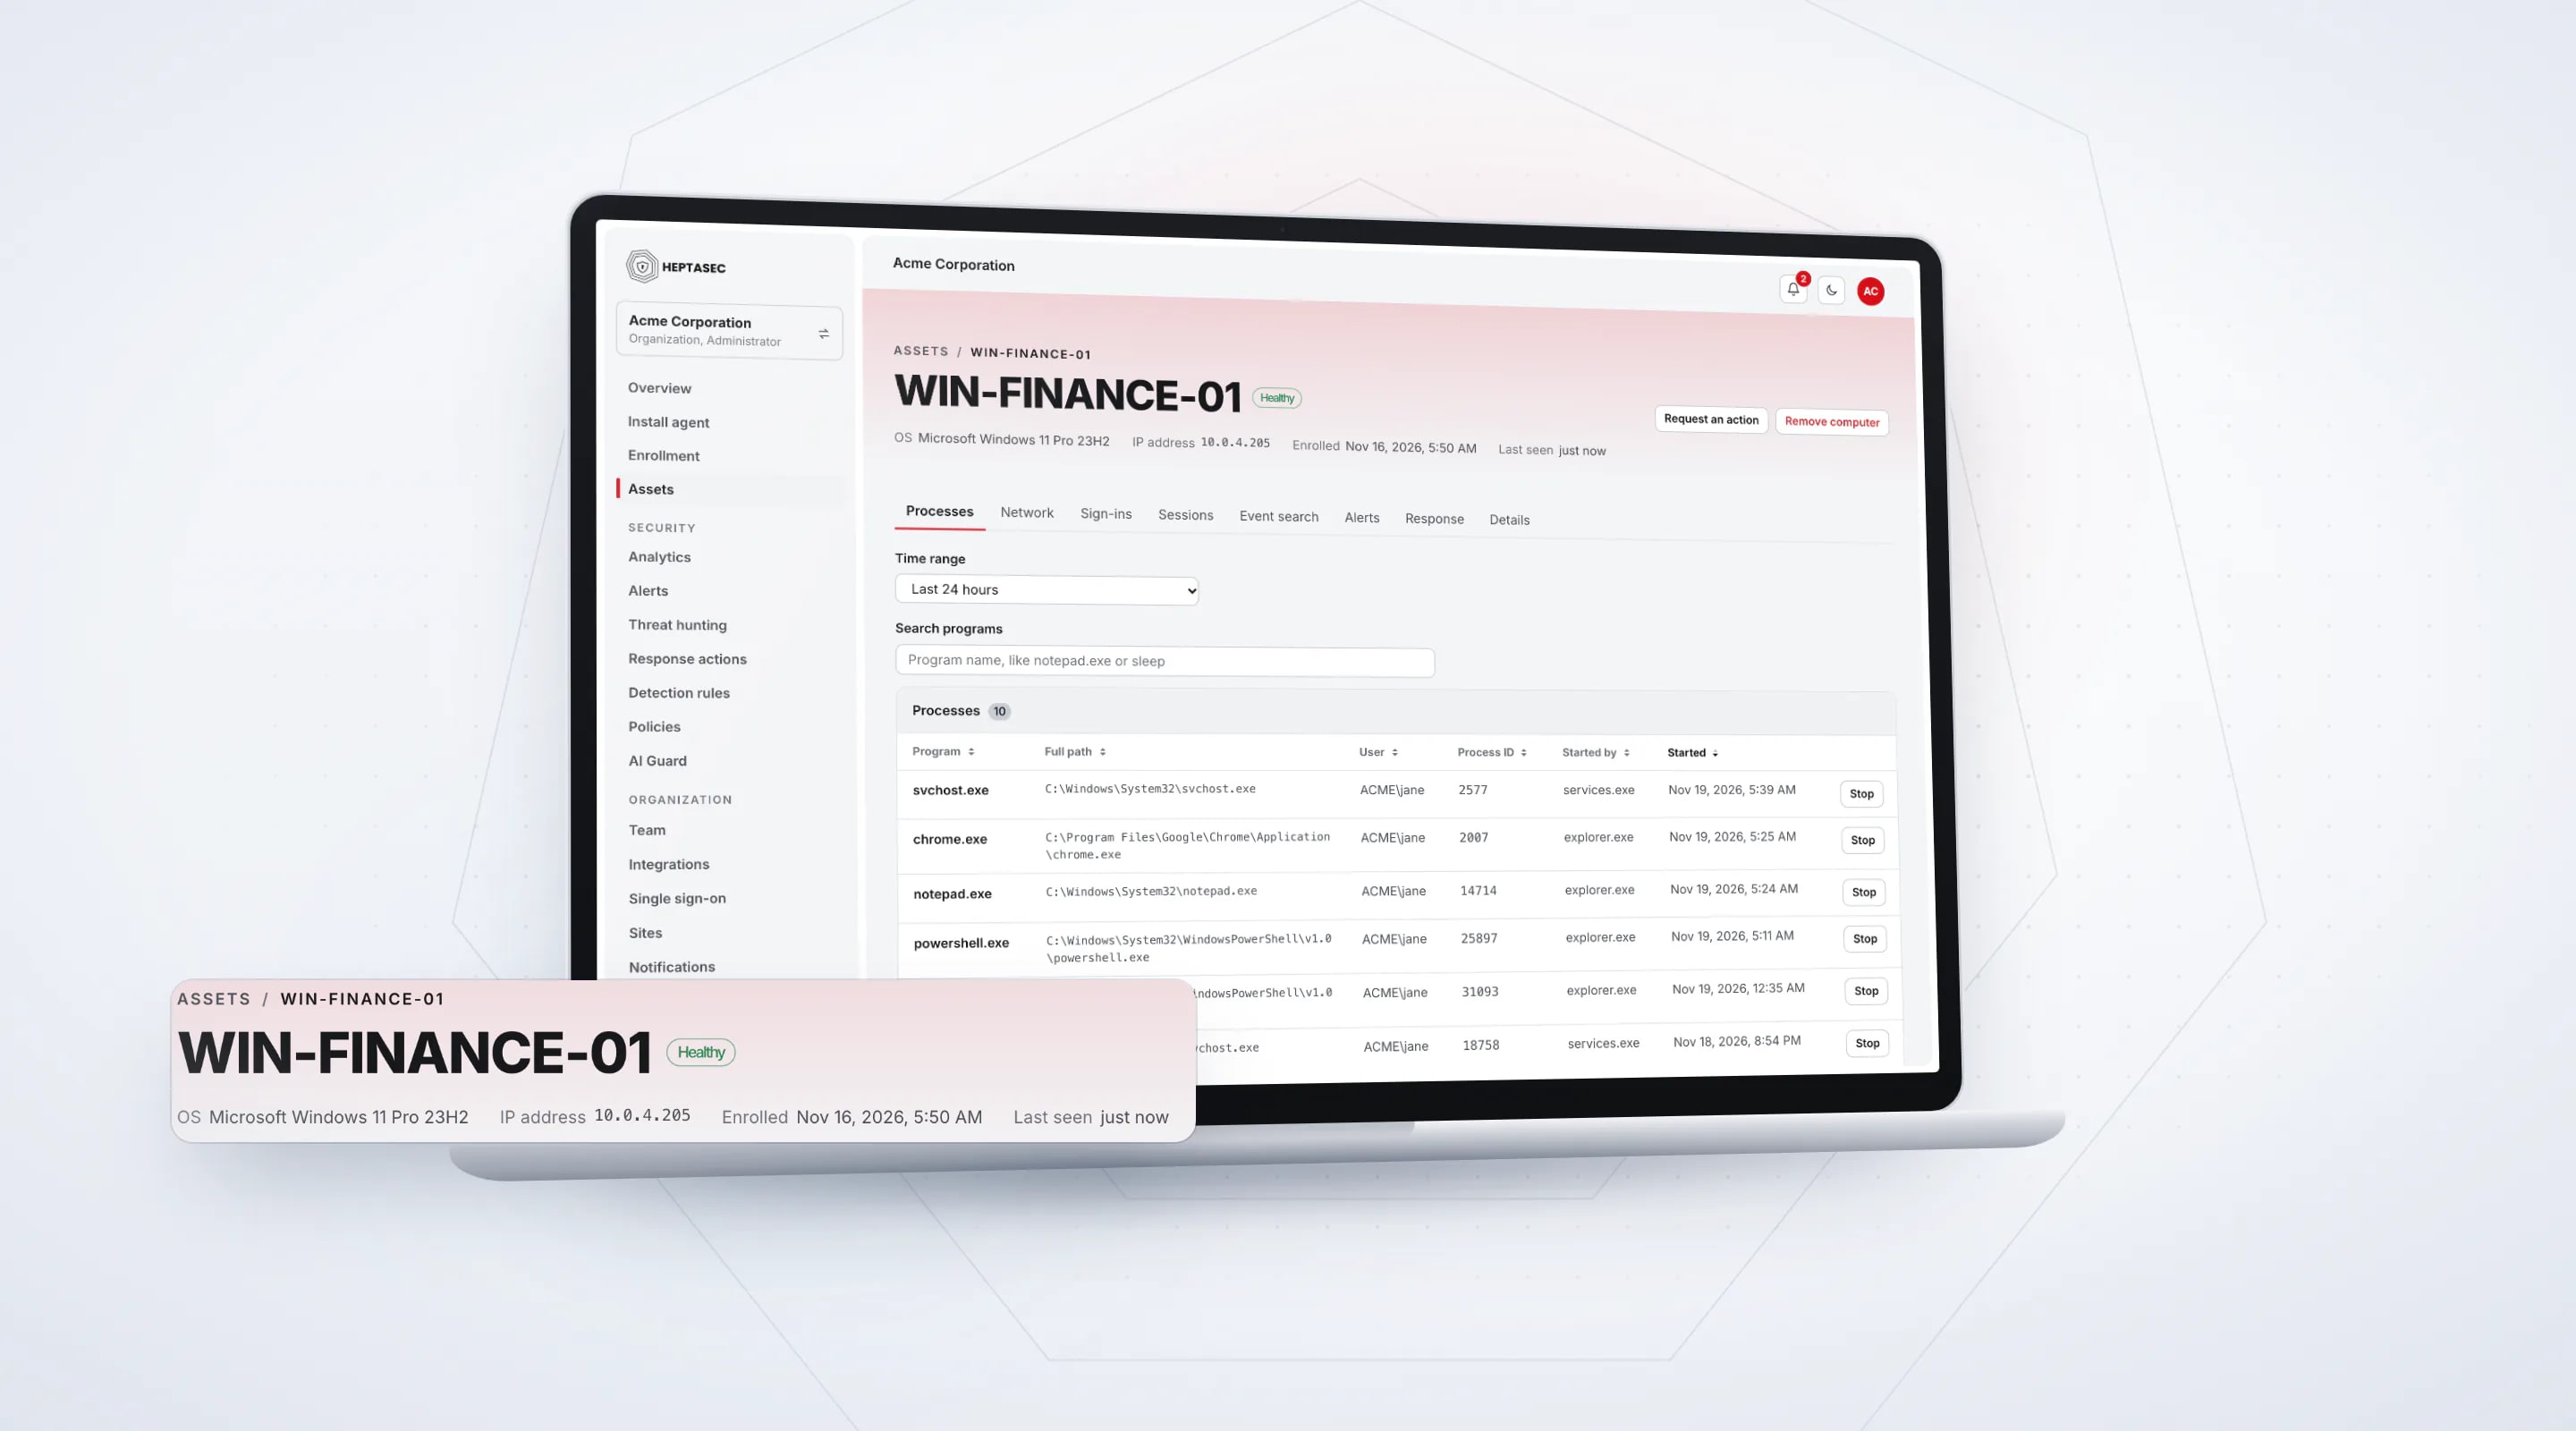
Our Extended Detection and Response platform brings together signals from endpoints, networks, cloud services, and identity systems into a single view, so threats that would slip past a single tool get caught by correlation across all of them.
Core capabilities
- Endpoint detection & response (Windows, macOS, Linux)
- Network traffic monitoring & anomaly detection
- Cloud and identity threat detection
- Automated correlation & alert prioritization
- Optional 24/7 managed monitoring (SOC-as-a-Service)
Built for every sector
- Banking & financial services
- Telecom (large, distributed infrastructure)
- Government & public sector
- SMEs & enterprises without an in-house SOC
- Single office to multi-country operations
02VAPT
Vulnerability Assessment & Penetration Testing
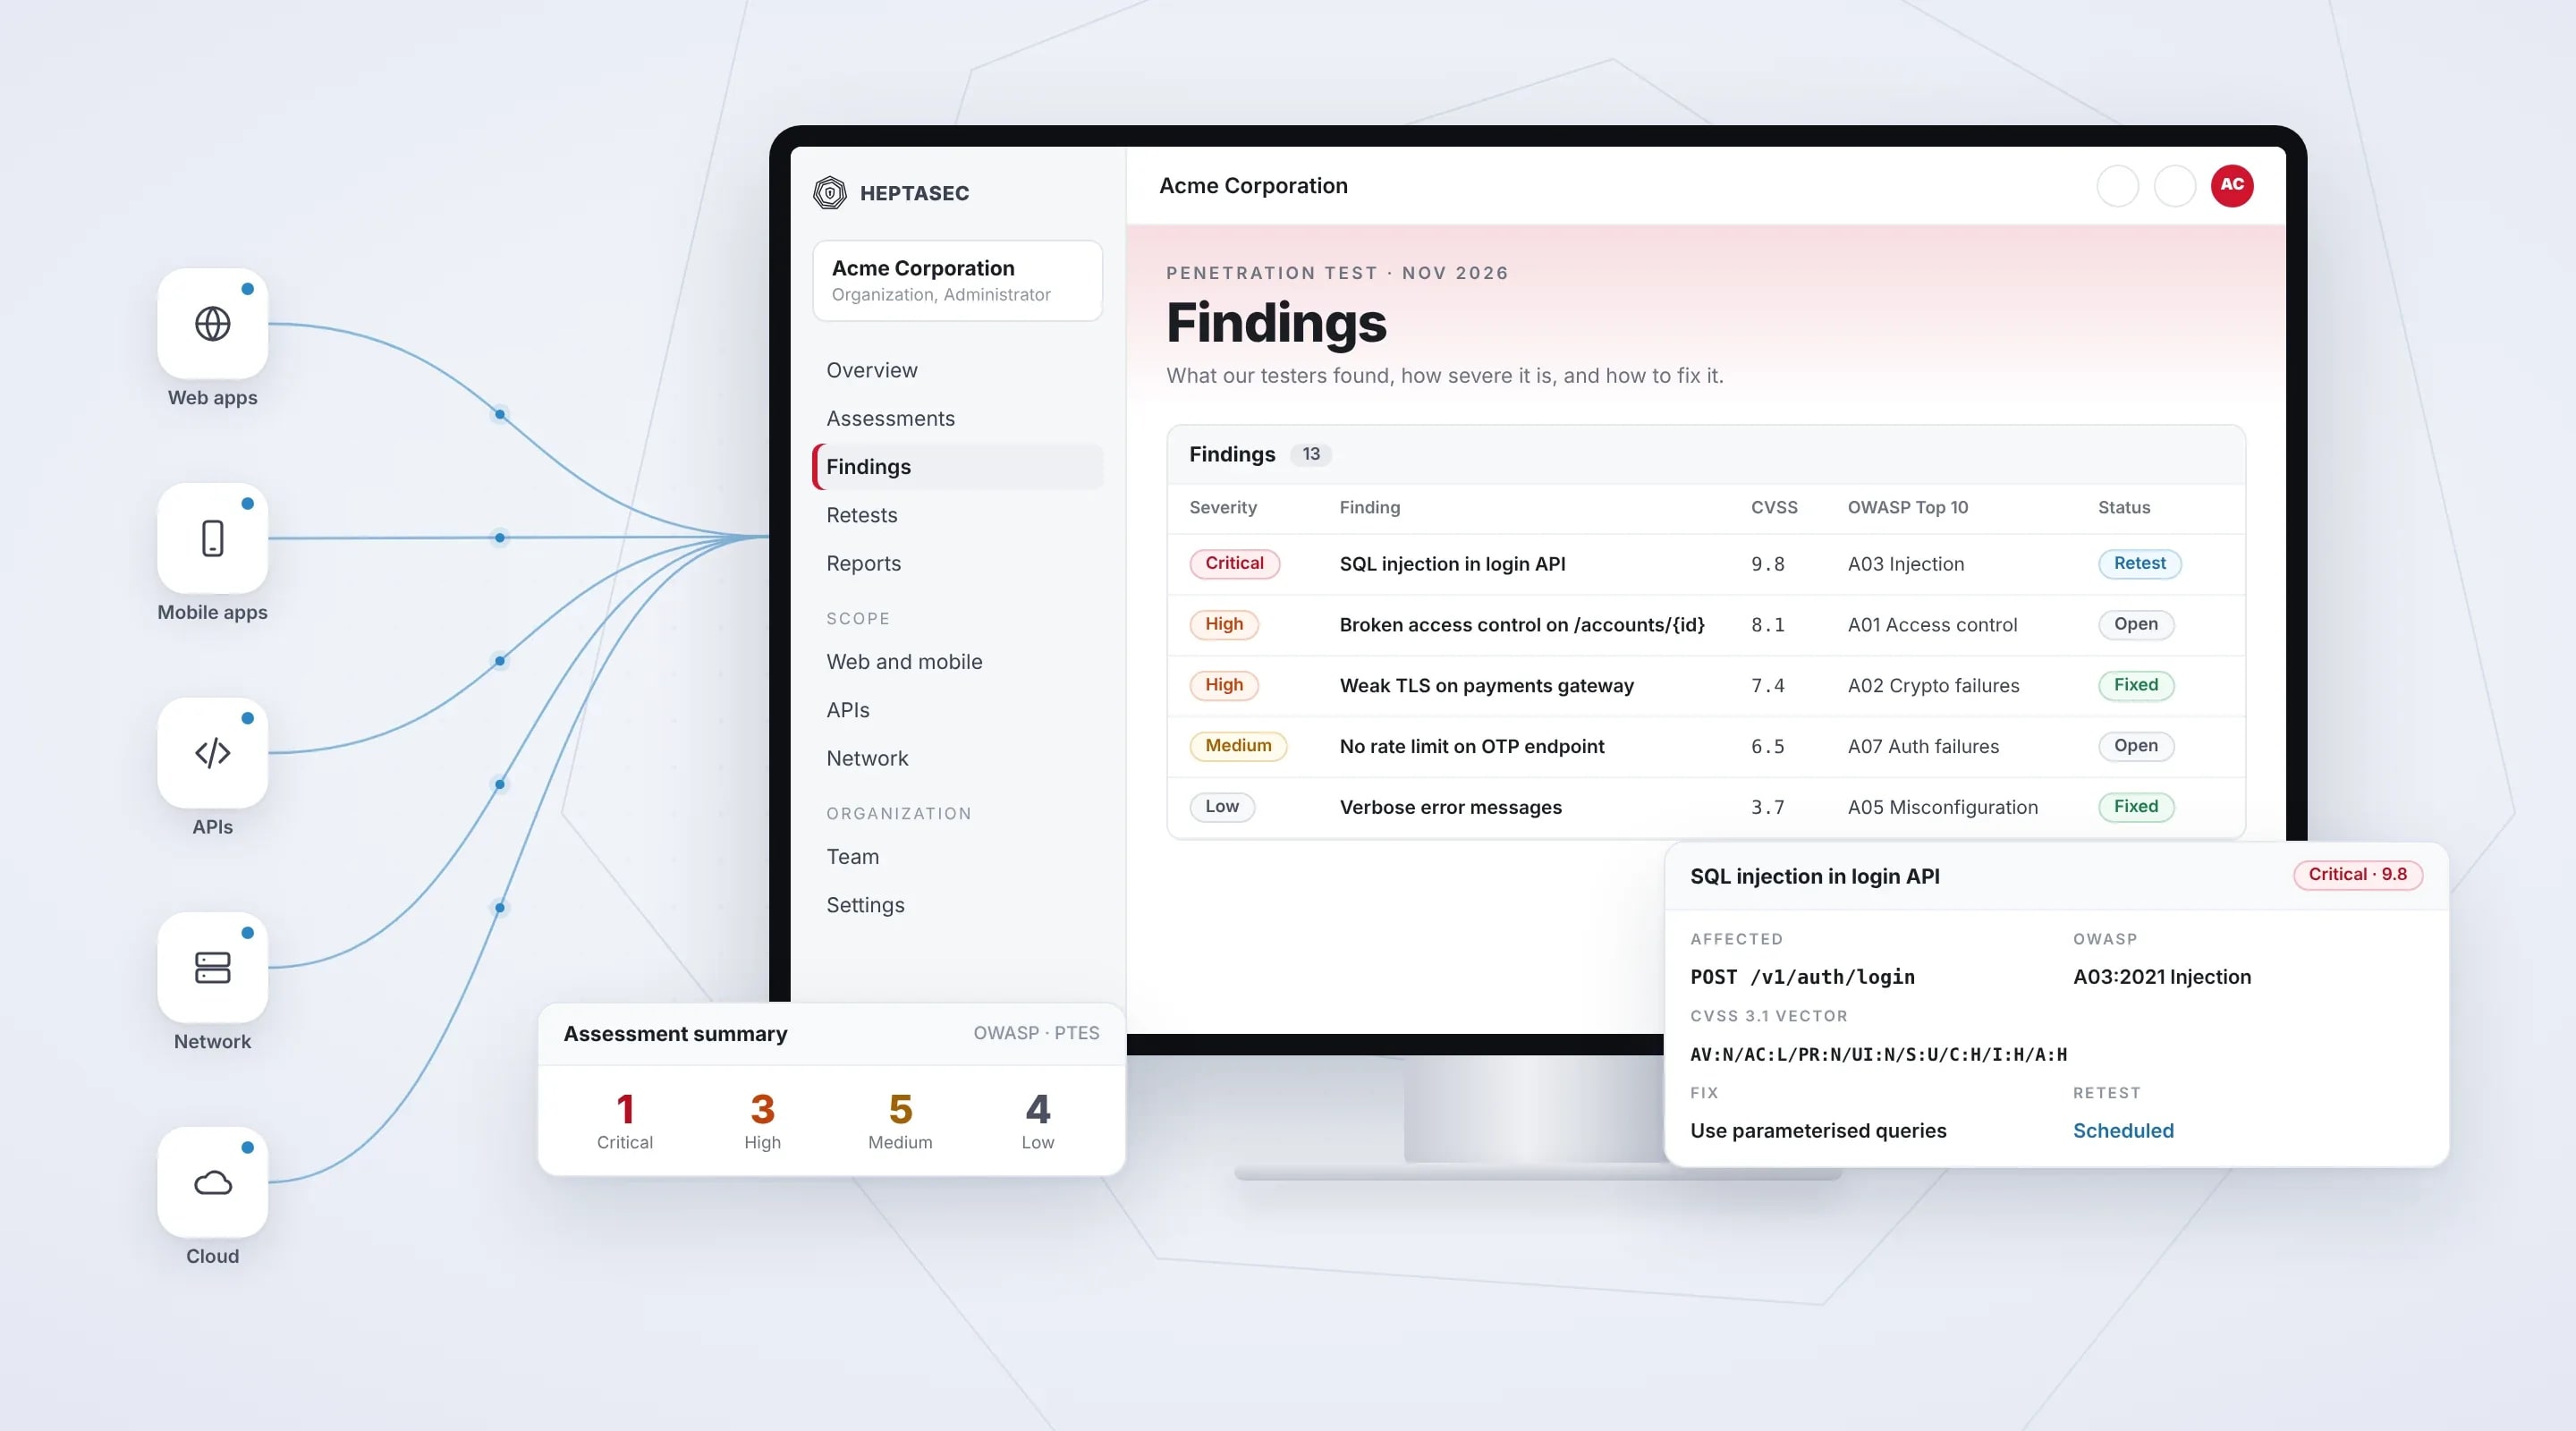
We simulate real attacker behaviour against your networks, applications, and infrastructure to find exploitable weaknesses before someone else does.
What's included
- External and internal network penetration testing
- Web and mobile application security testing
- Active Directory and infrastructure assessments
- Social engineering and phishing simulations
- Wireless network security testing
Why it matters
A penetration test doesn't just satisfy a checkbox — it's the evidence base for every other decision you'll make about where to invest in security next. We rate every finding by likelihood and business impact, the same way we'd defend it in front of your board.
Deliverables
- Plain-language executive summary
- Full technical findings with proof-of-concept evidence
- Risk-rated findings
- A prioritized remediation roadmap
- Free retest of Critical/High findings
03Compliance
Security Audits & Compliance Readiness
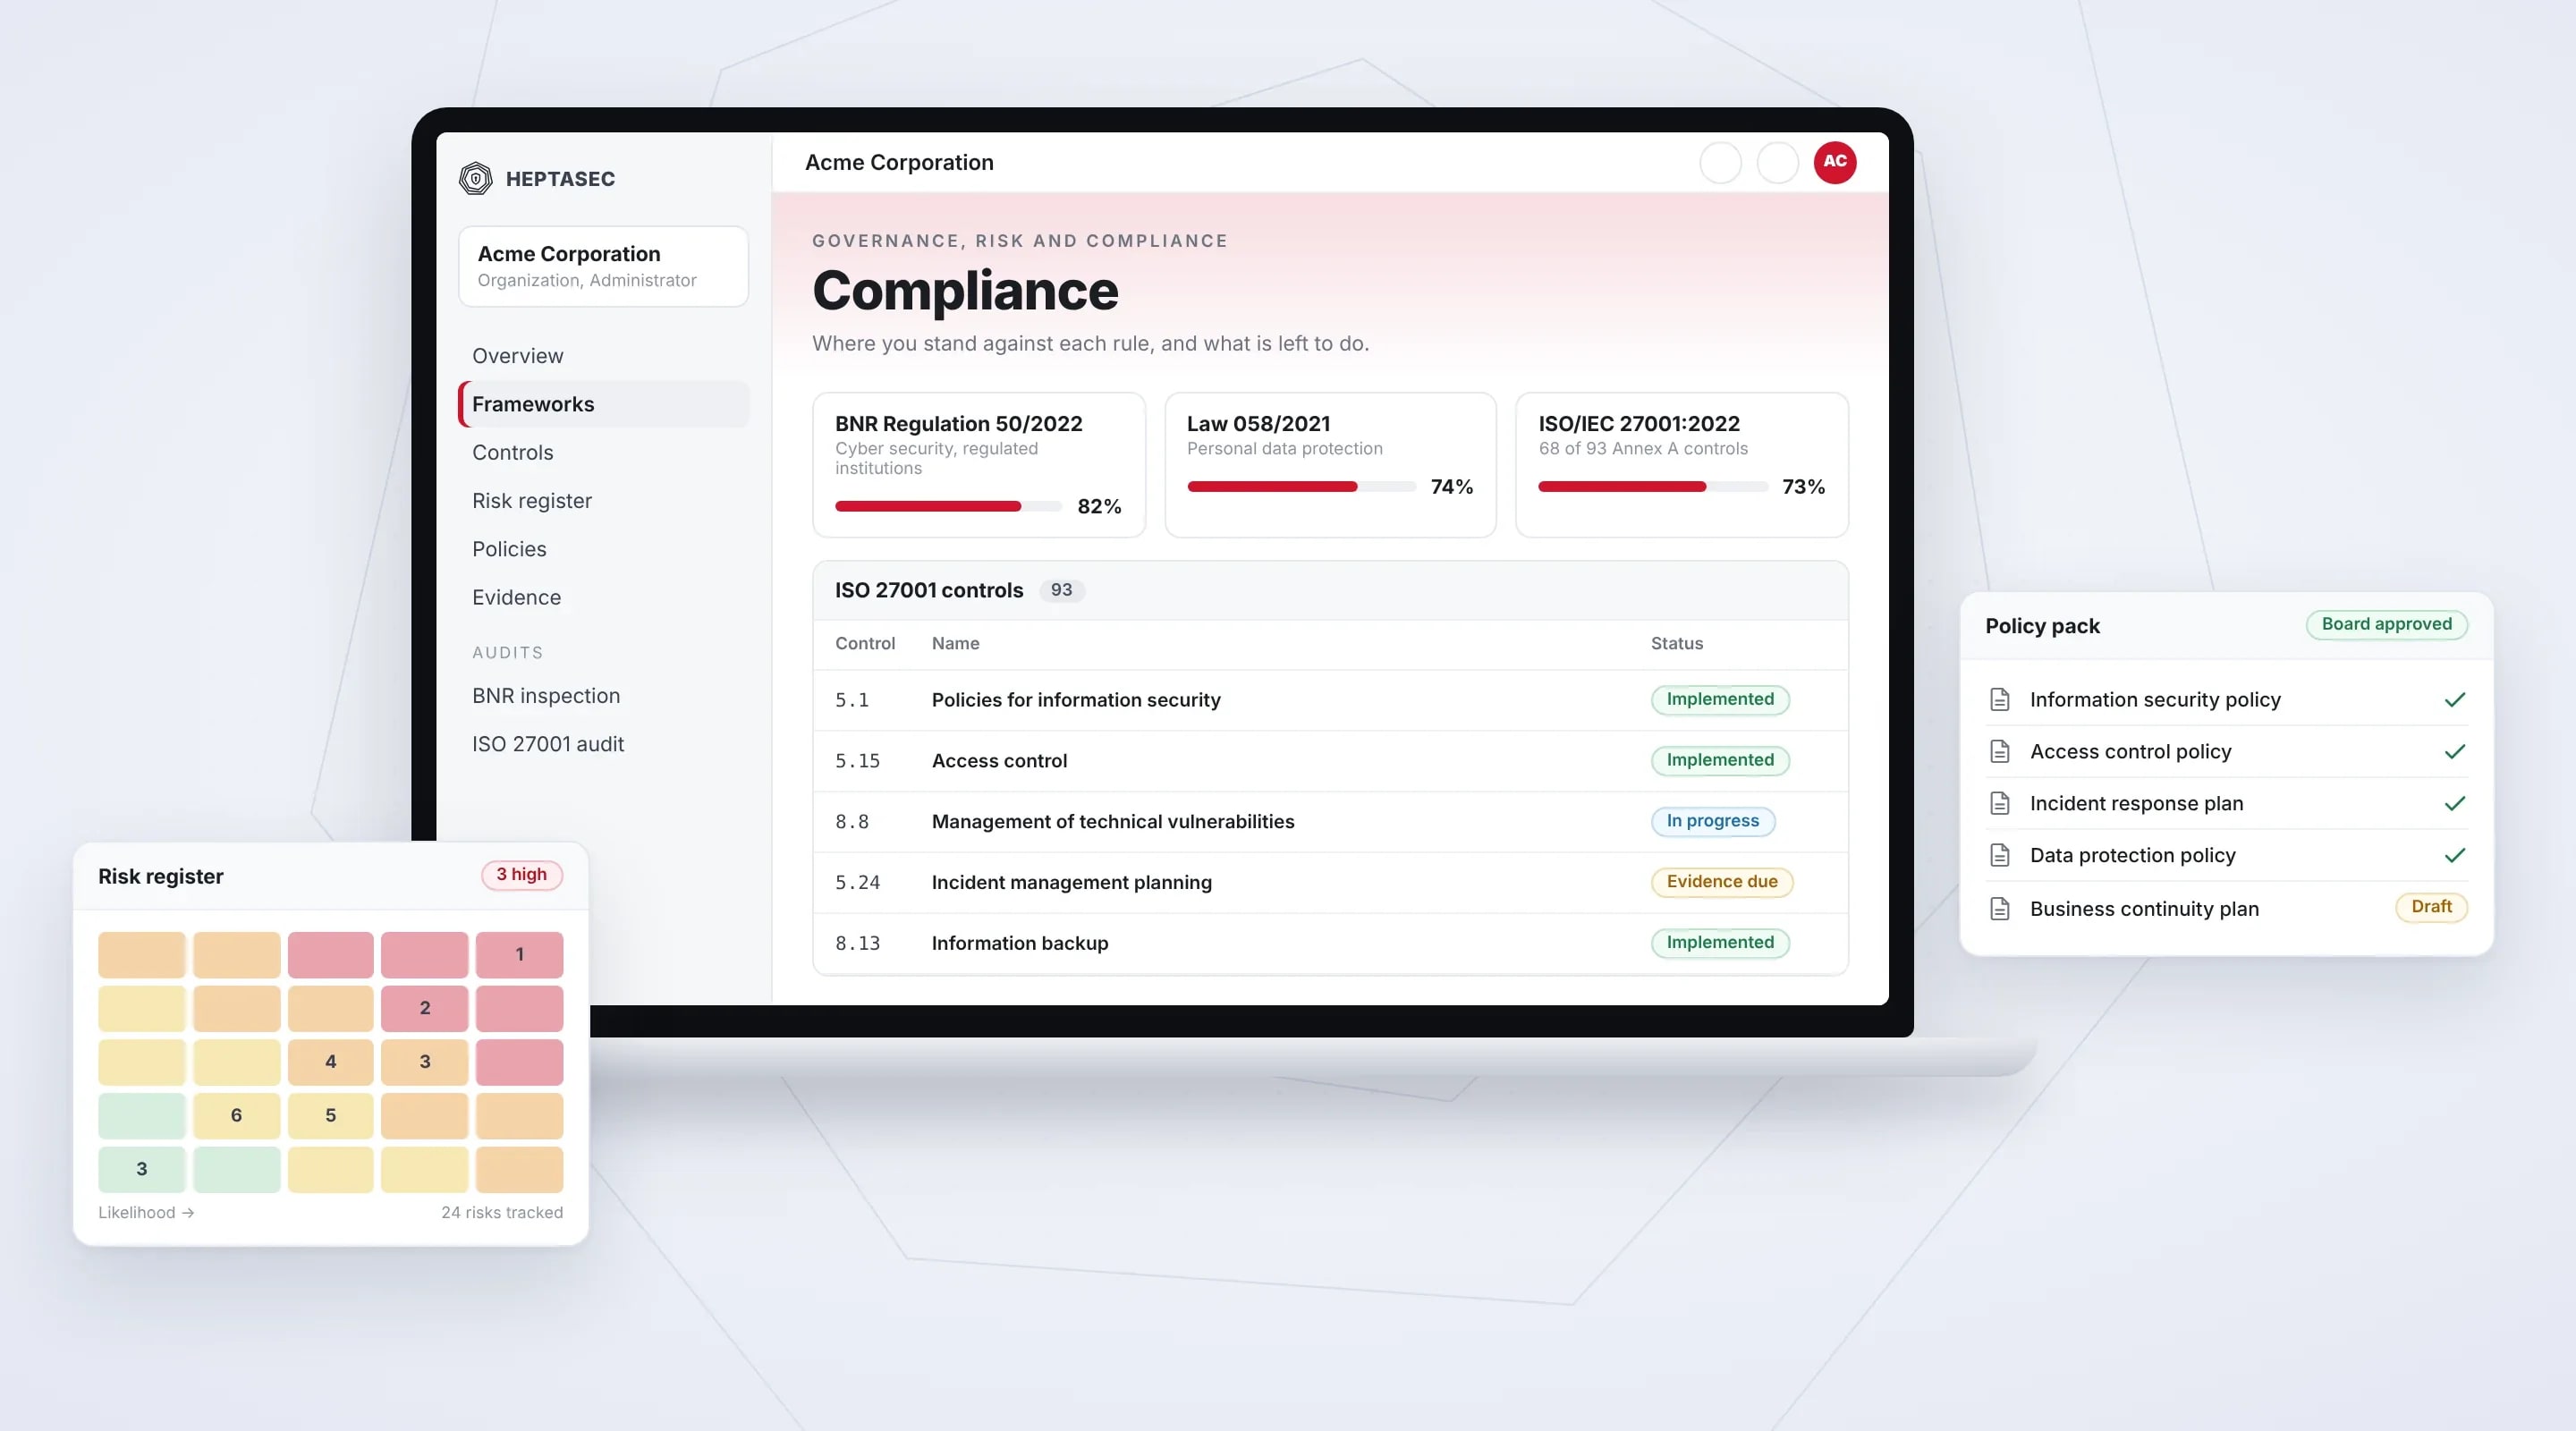
We prepare organizations for ISO/IEC 27001 certification and for audits by local regulators, building the governance structure and evidence base auditors and leadership can trust.
What's included
- ISO/IEC 27001:2022 gap assessment & ISMS design
- Risk assessment and risk treatment planning
- Statement of Applicability development
- Stage 1 & 2 certification-audit preparation
- Regulatory compliance mapping, DPIA & RoPA support
Why it matters
Compliance and security are not the same thing, but they should reinforce each other. We build compliance programs on top of real security work, so you're not just passing an audit — you're actually reducing risk.
Our regulatory audit support extends to regulator engagement, evidence preparation, and remediation tracking through to audit closure.
04Remediation
Remediation
Finding the problem is only half the job. Our remediation service fixes what a Health Check, VAPT or audit uncovers — configuration, hardening, access control, backups, monitoring and policy — so your risk actually goes down, not just your risk report.
What's included
- Remediation plan built from your findings
- Security configuration changes and system hardening
- Access-control and identity improvements
- Backup and monitoring improvements
- Verification testing once fixes are in place
Why it matters
An assessment tells you what's wrong. Remediation is where the risk actually goes away. We scope and price it by the work required, never as open-ended consulting hours.
Deliverables
- Remediation report
- Verification/retest of fixed issues
05Training
Security Awareness Training
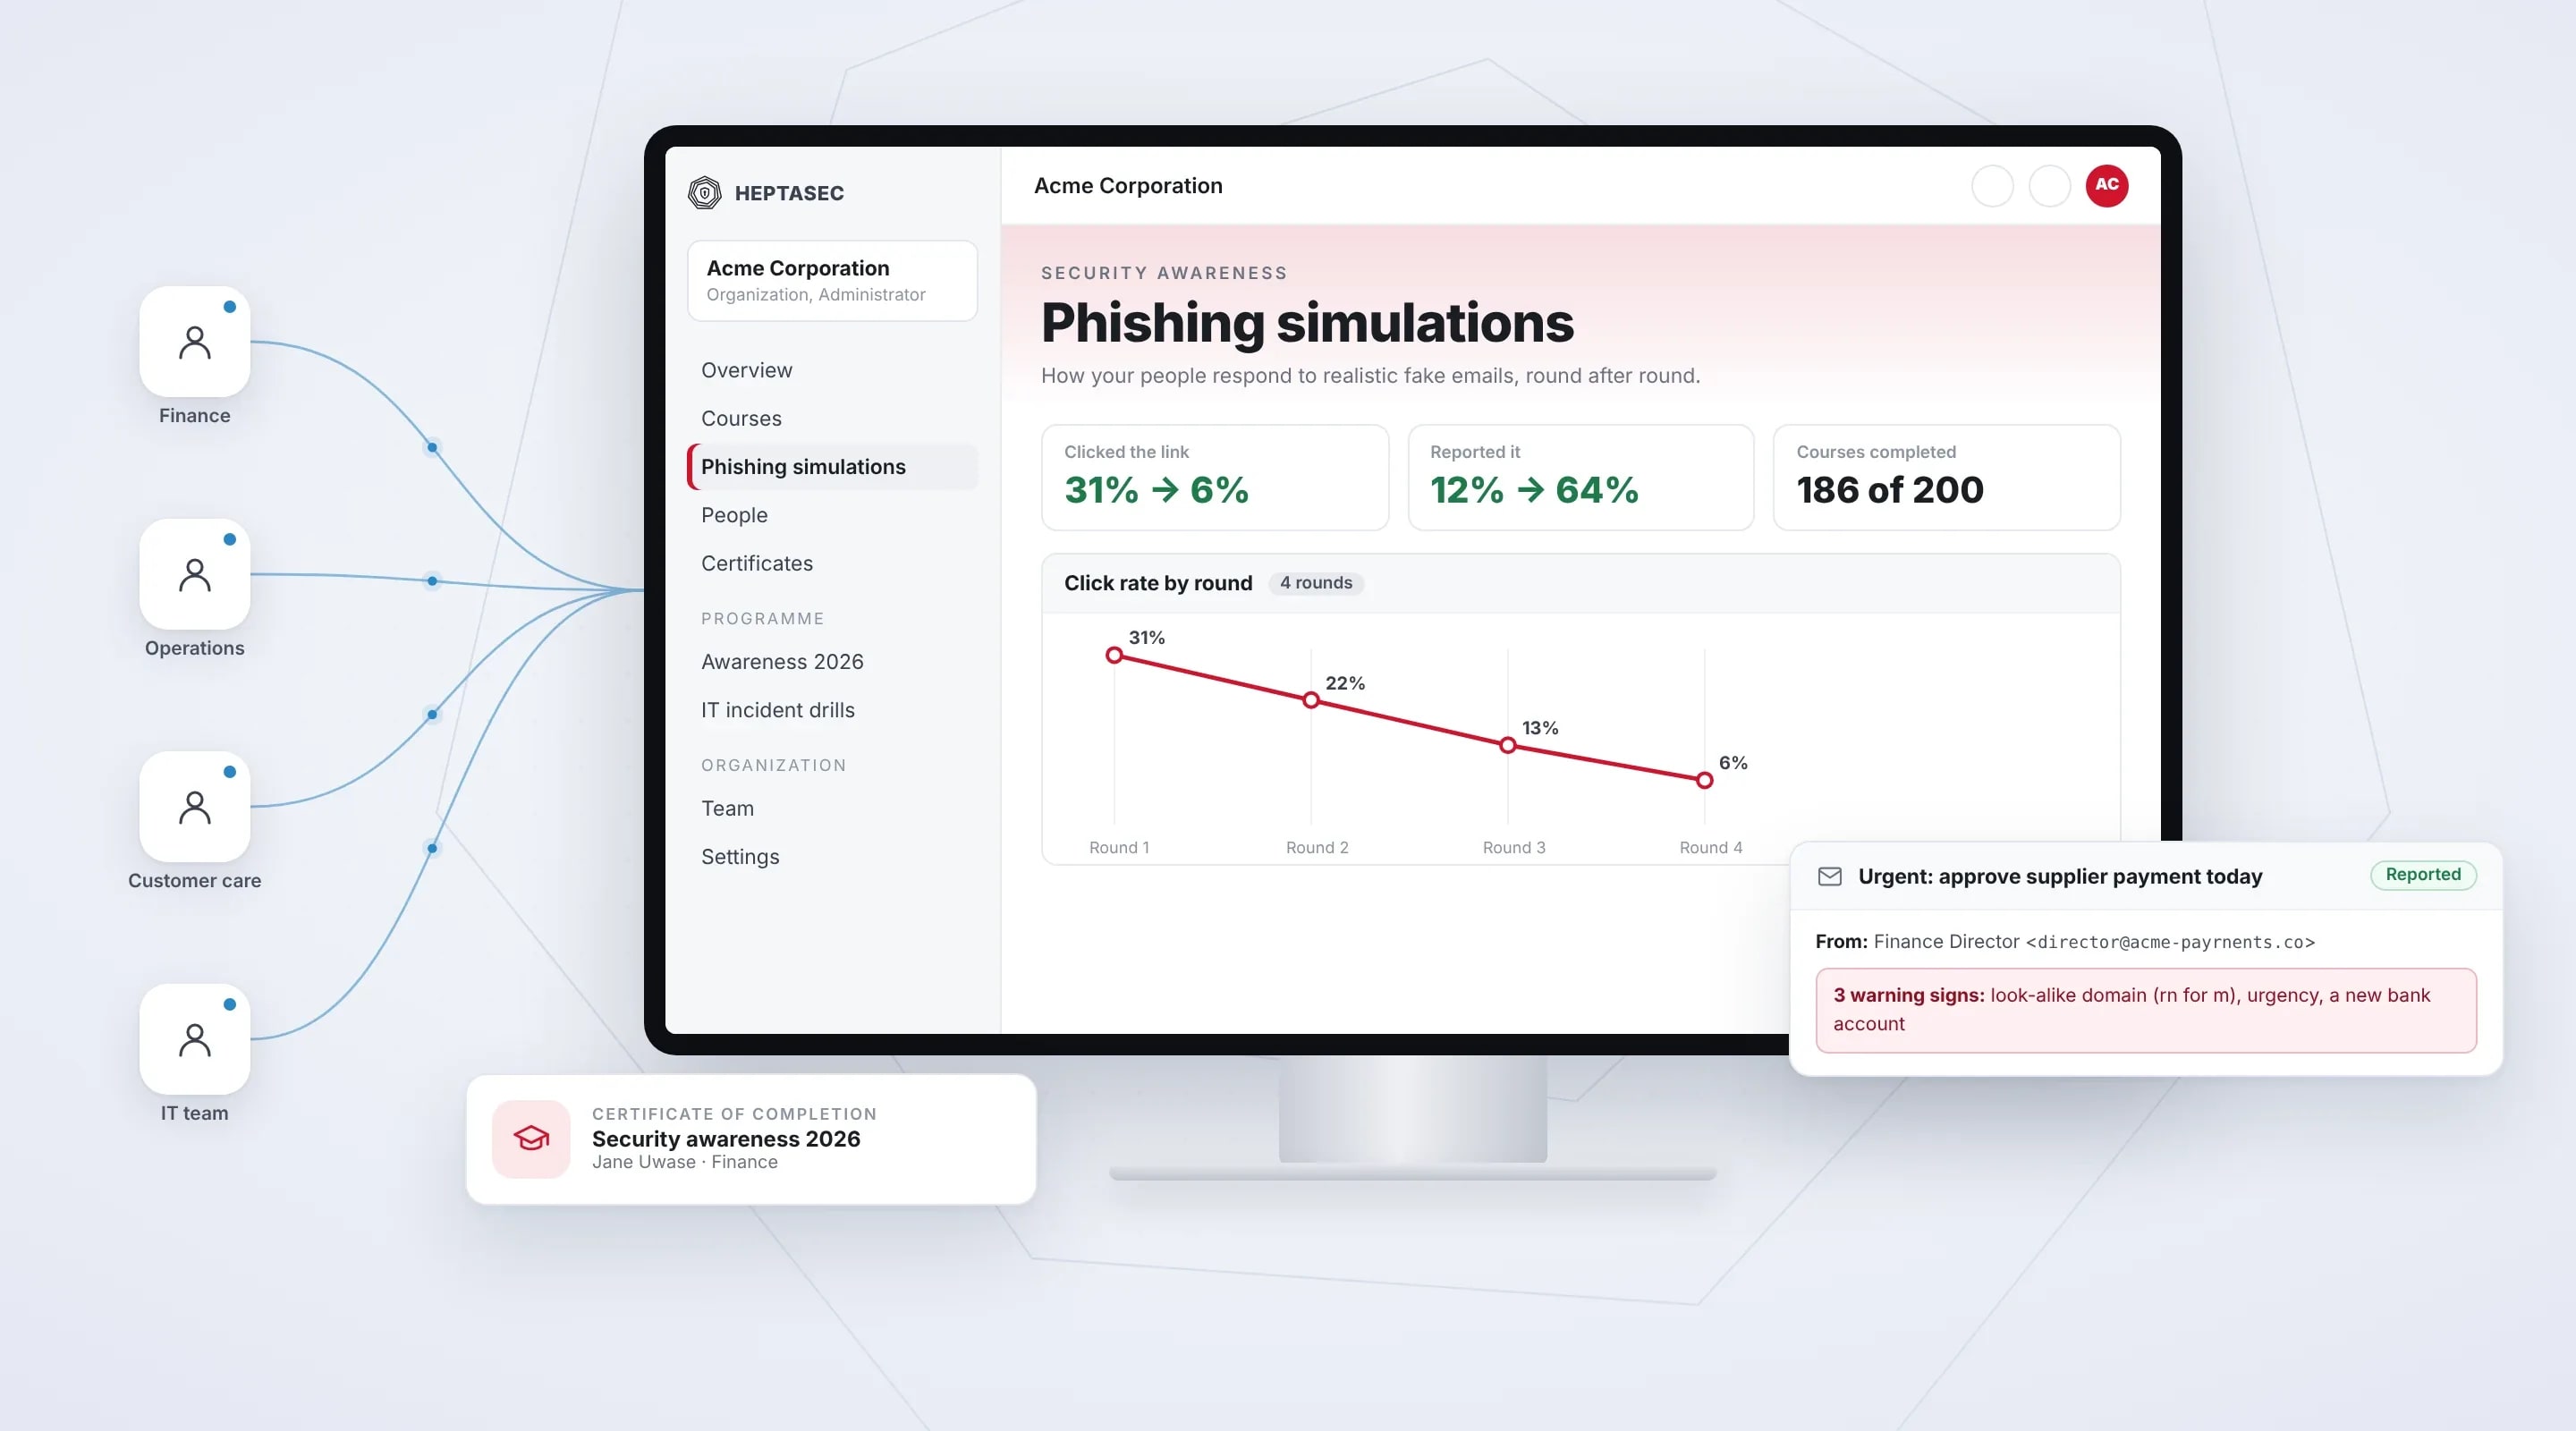
Most breaches start with a person, not a system. We build training programs that change staff behaviour, not one-off slideshows people forget the following week.
What's included
- Role-based training for staff, IT, and leadership
- Simulated phishing campaigns with real metrics
- Live and recorded training sessions
- Custom scenarios based on your industry
- Ongoing awareness campaigns, not annual events
Why it matters
Every technical control we help you build can be undone by one convincing email. Awareness training is the cheapest, highest-return investment in your entire security program.
Outcomes we track over time
- Phishing click-through and reporting rates
- Staff confidence
- Incident-reporting speed and accuracy
06Health Check
Cybersecurity Health Check
Most organizations don't need a full penetration test to start — they need a clear, honest picture of where they stand. Our Health Check reviews your identity, endpoint, network, backup, monitoring and data protection practices and hands you a prioritized plan.
What's included
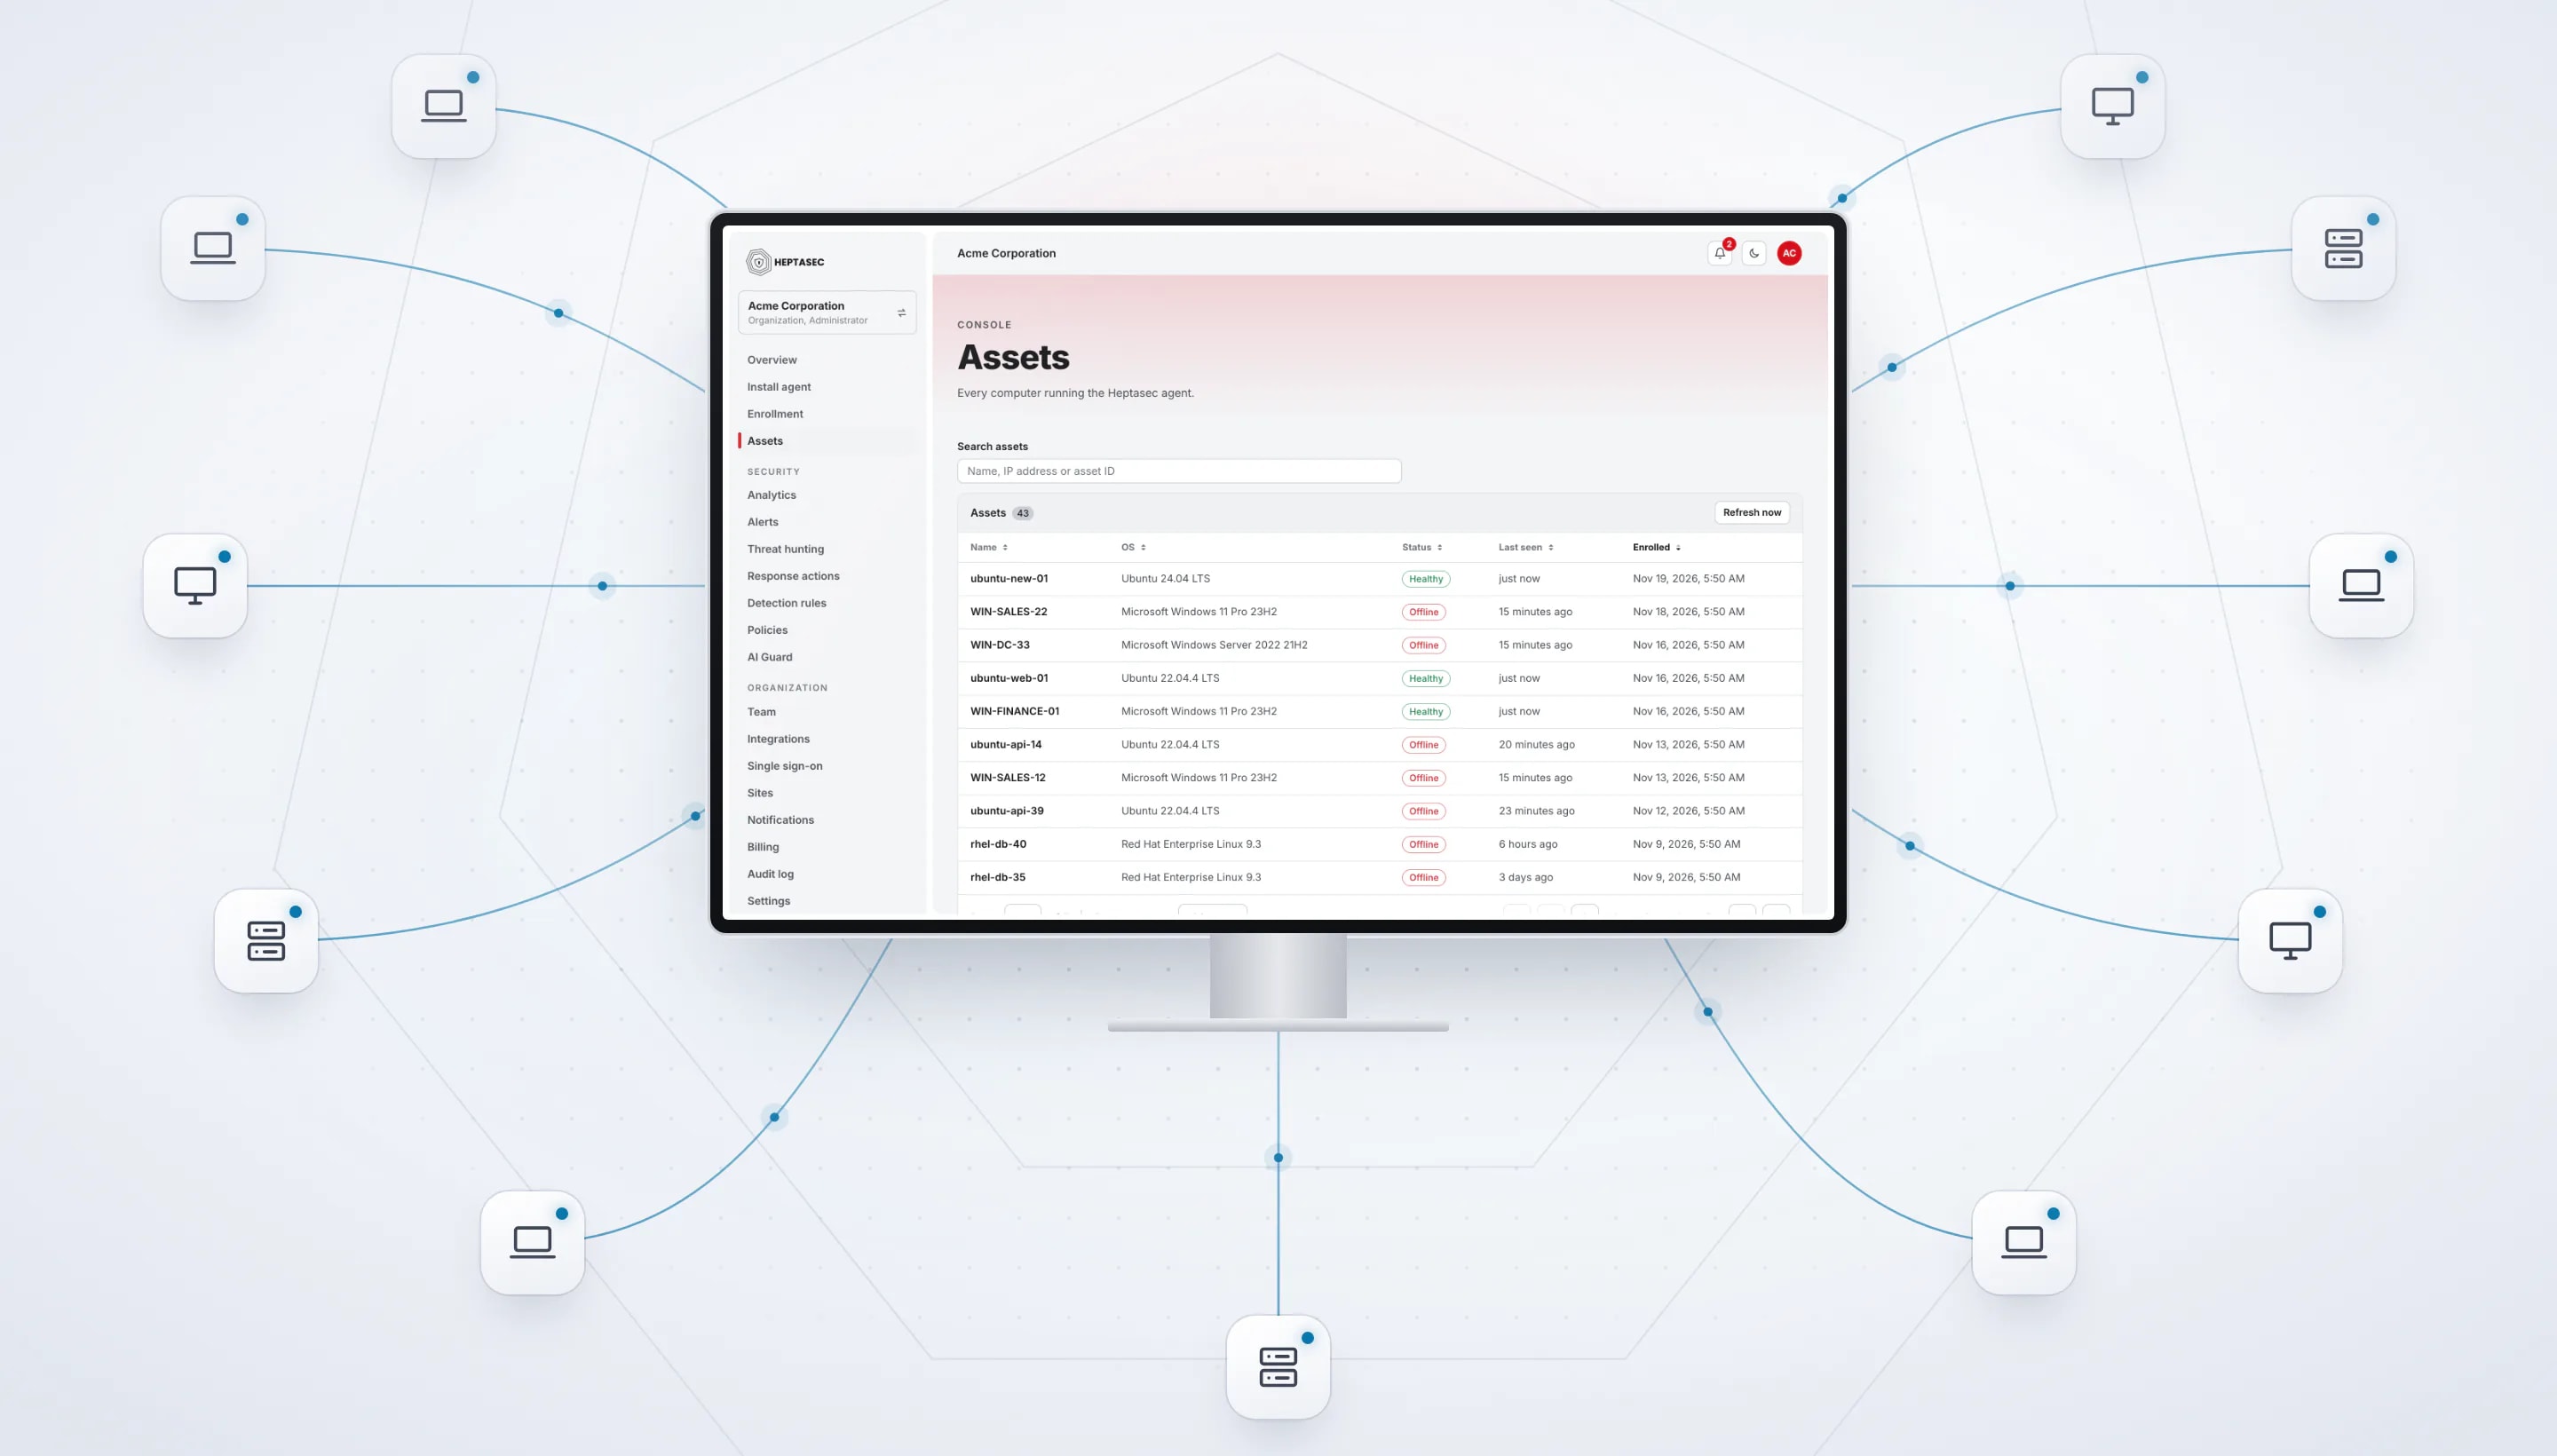
- Asset and technology review
- Network, identity, endpoint and cloud review
- Data protection and backup review
- Logging, monitoring and incident-response review
- Policy, governance and security-awareness review
Why it matters
You can't fix what you haven't measured. The Health Check gives you a security score, a risk register and a 90-day roadmap — in plain language your leadership team can act on, not a wall of jargon.
Deliverables
- Executive summary
- Risk register
- Security score
- 90-day prioritized roadmap