
0
holders
CEH
- Rwagatare King
- Mireille Ukeye
- John Bright Rubayiza
- Nadine Muhimpundu
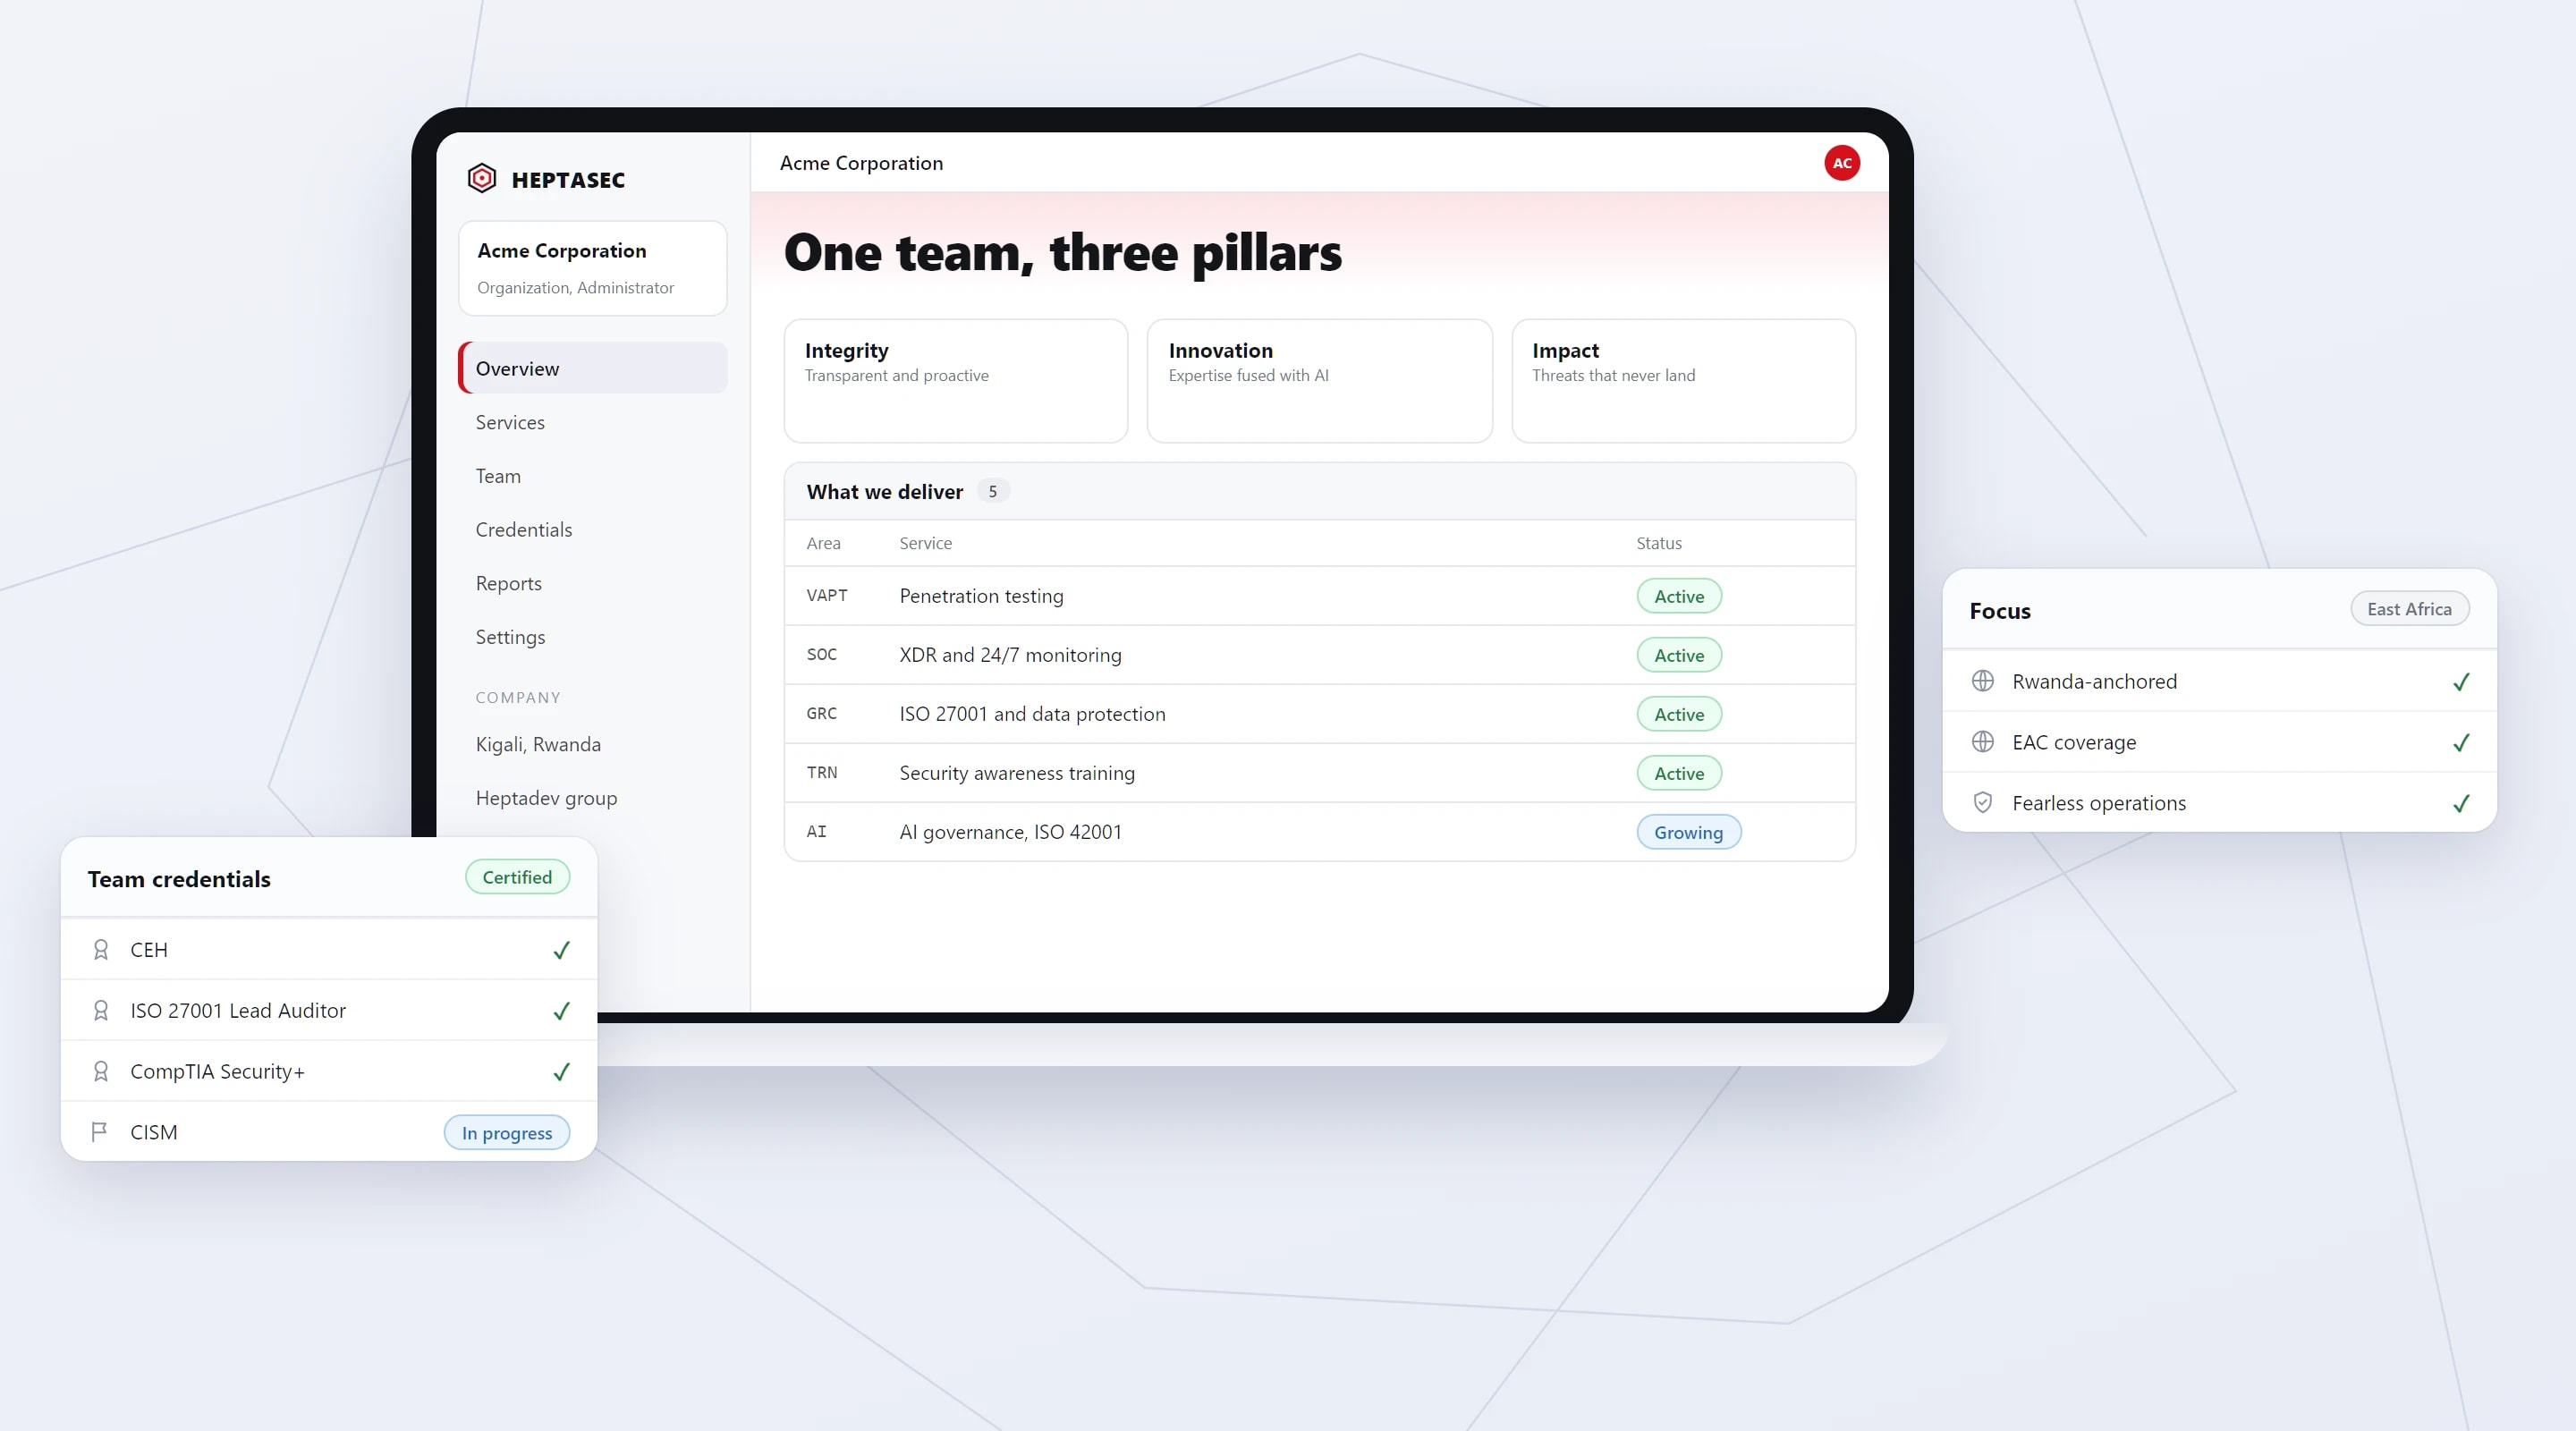
A Heptadev company blending AI with deep security expertise: VAPT, SOC and GRC under one roof, keeping you ahead of modern threats.
Empower businesses to operate fearlessly in a connected world, anticipating threats before they ever touch your systems.
Rwanda-anchored · East African Community focus
Founded by a team with a background in software engineering and offensive security, to close the gap between Africa's fast-growing digital economy and its thin cybersecurity coverage.
01
Offensive security testing against production financial and enterprise environments
02
ISO/IEC 27001 readiness and certification support
03
Regulatory audit support and data-protection compliance mapping
04
Security awareness and phishing-simulation programs at every staff level
05
Design, build and hardening of an in-house XDR detection platform
Transparent, proactive, and always a step ahead.
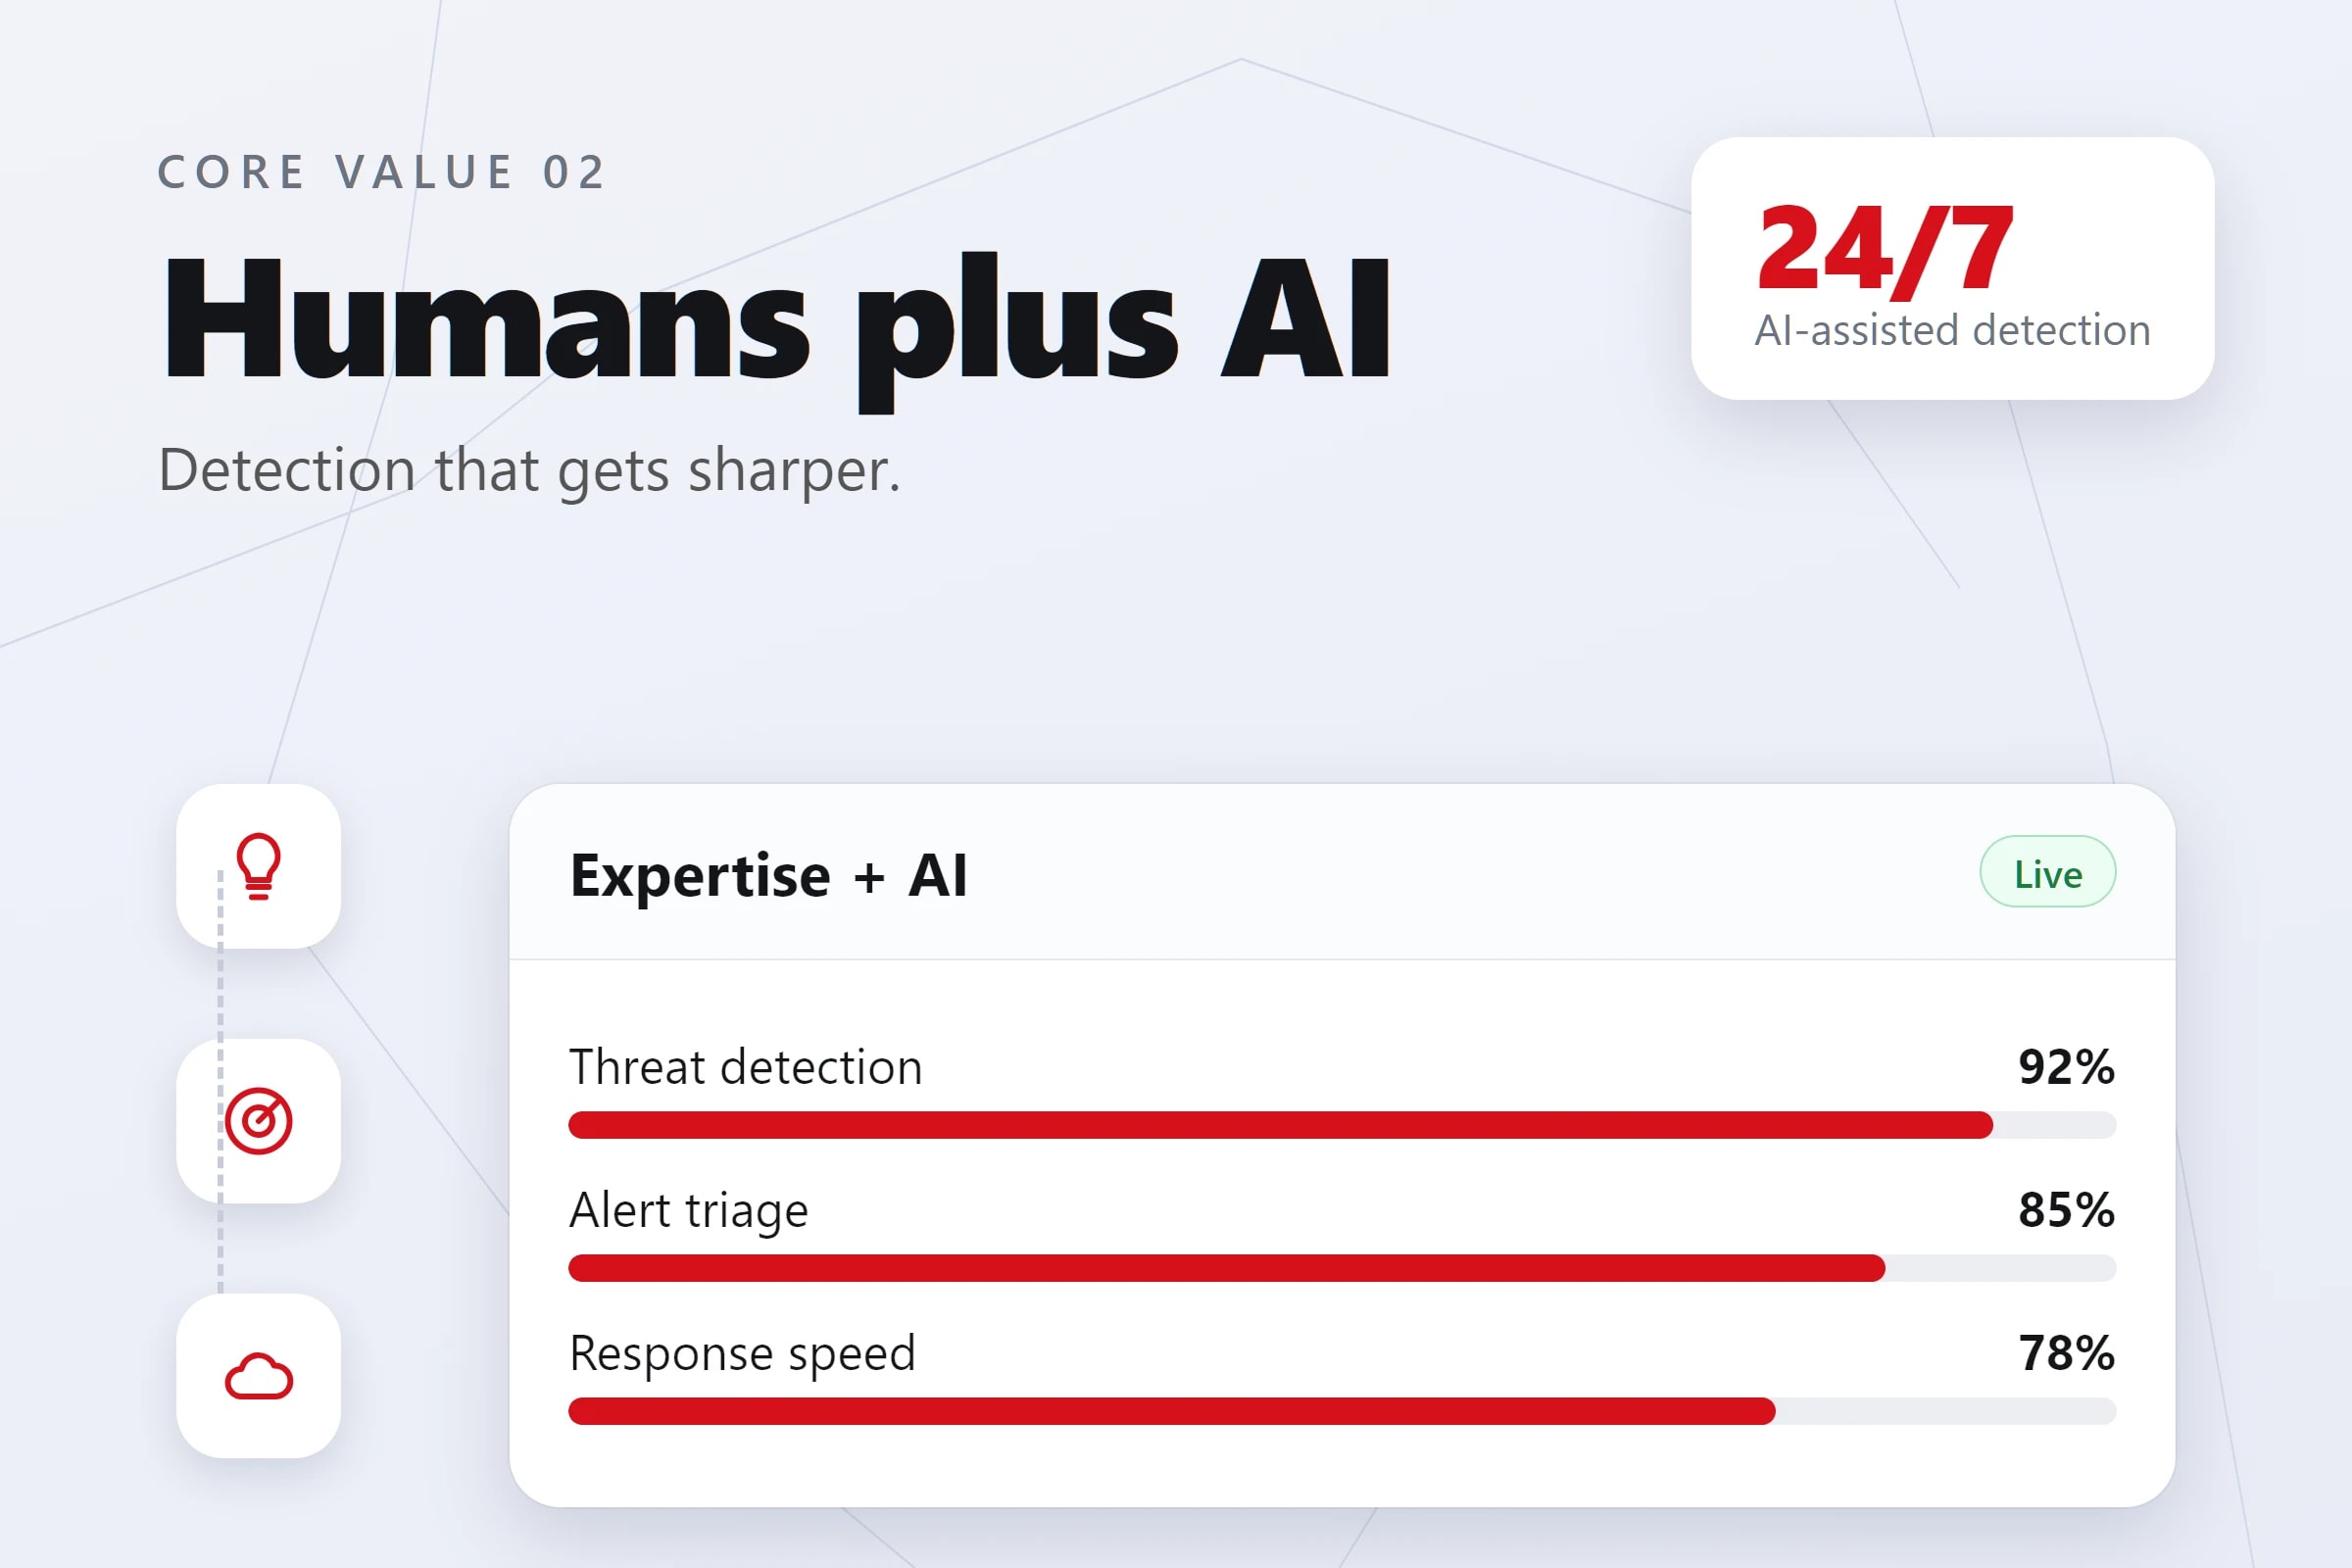
Deep technical expertise fused with cutting-edge AI.
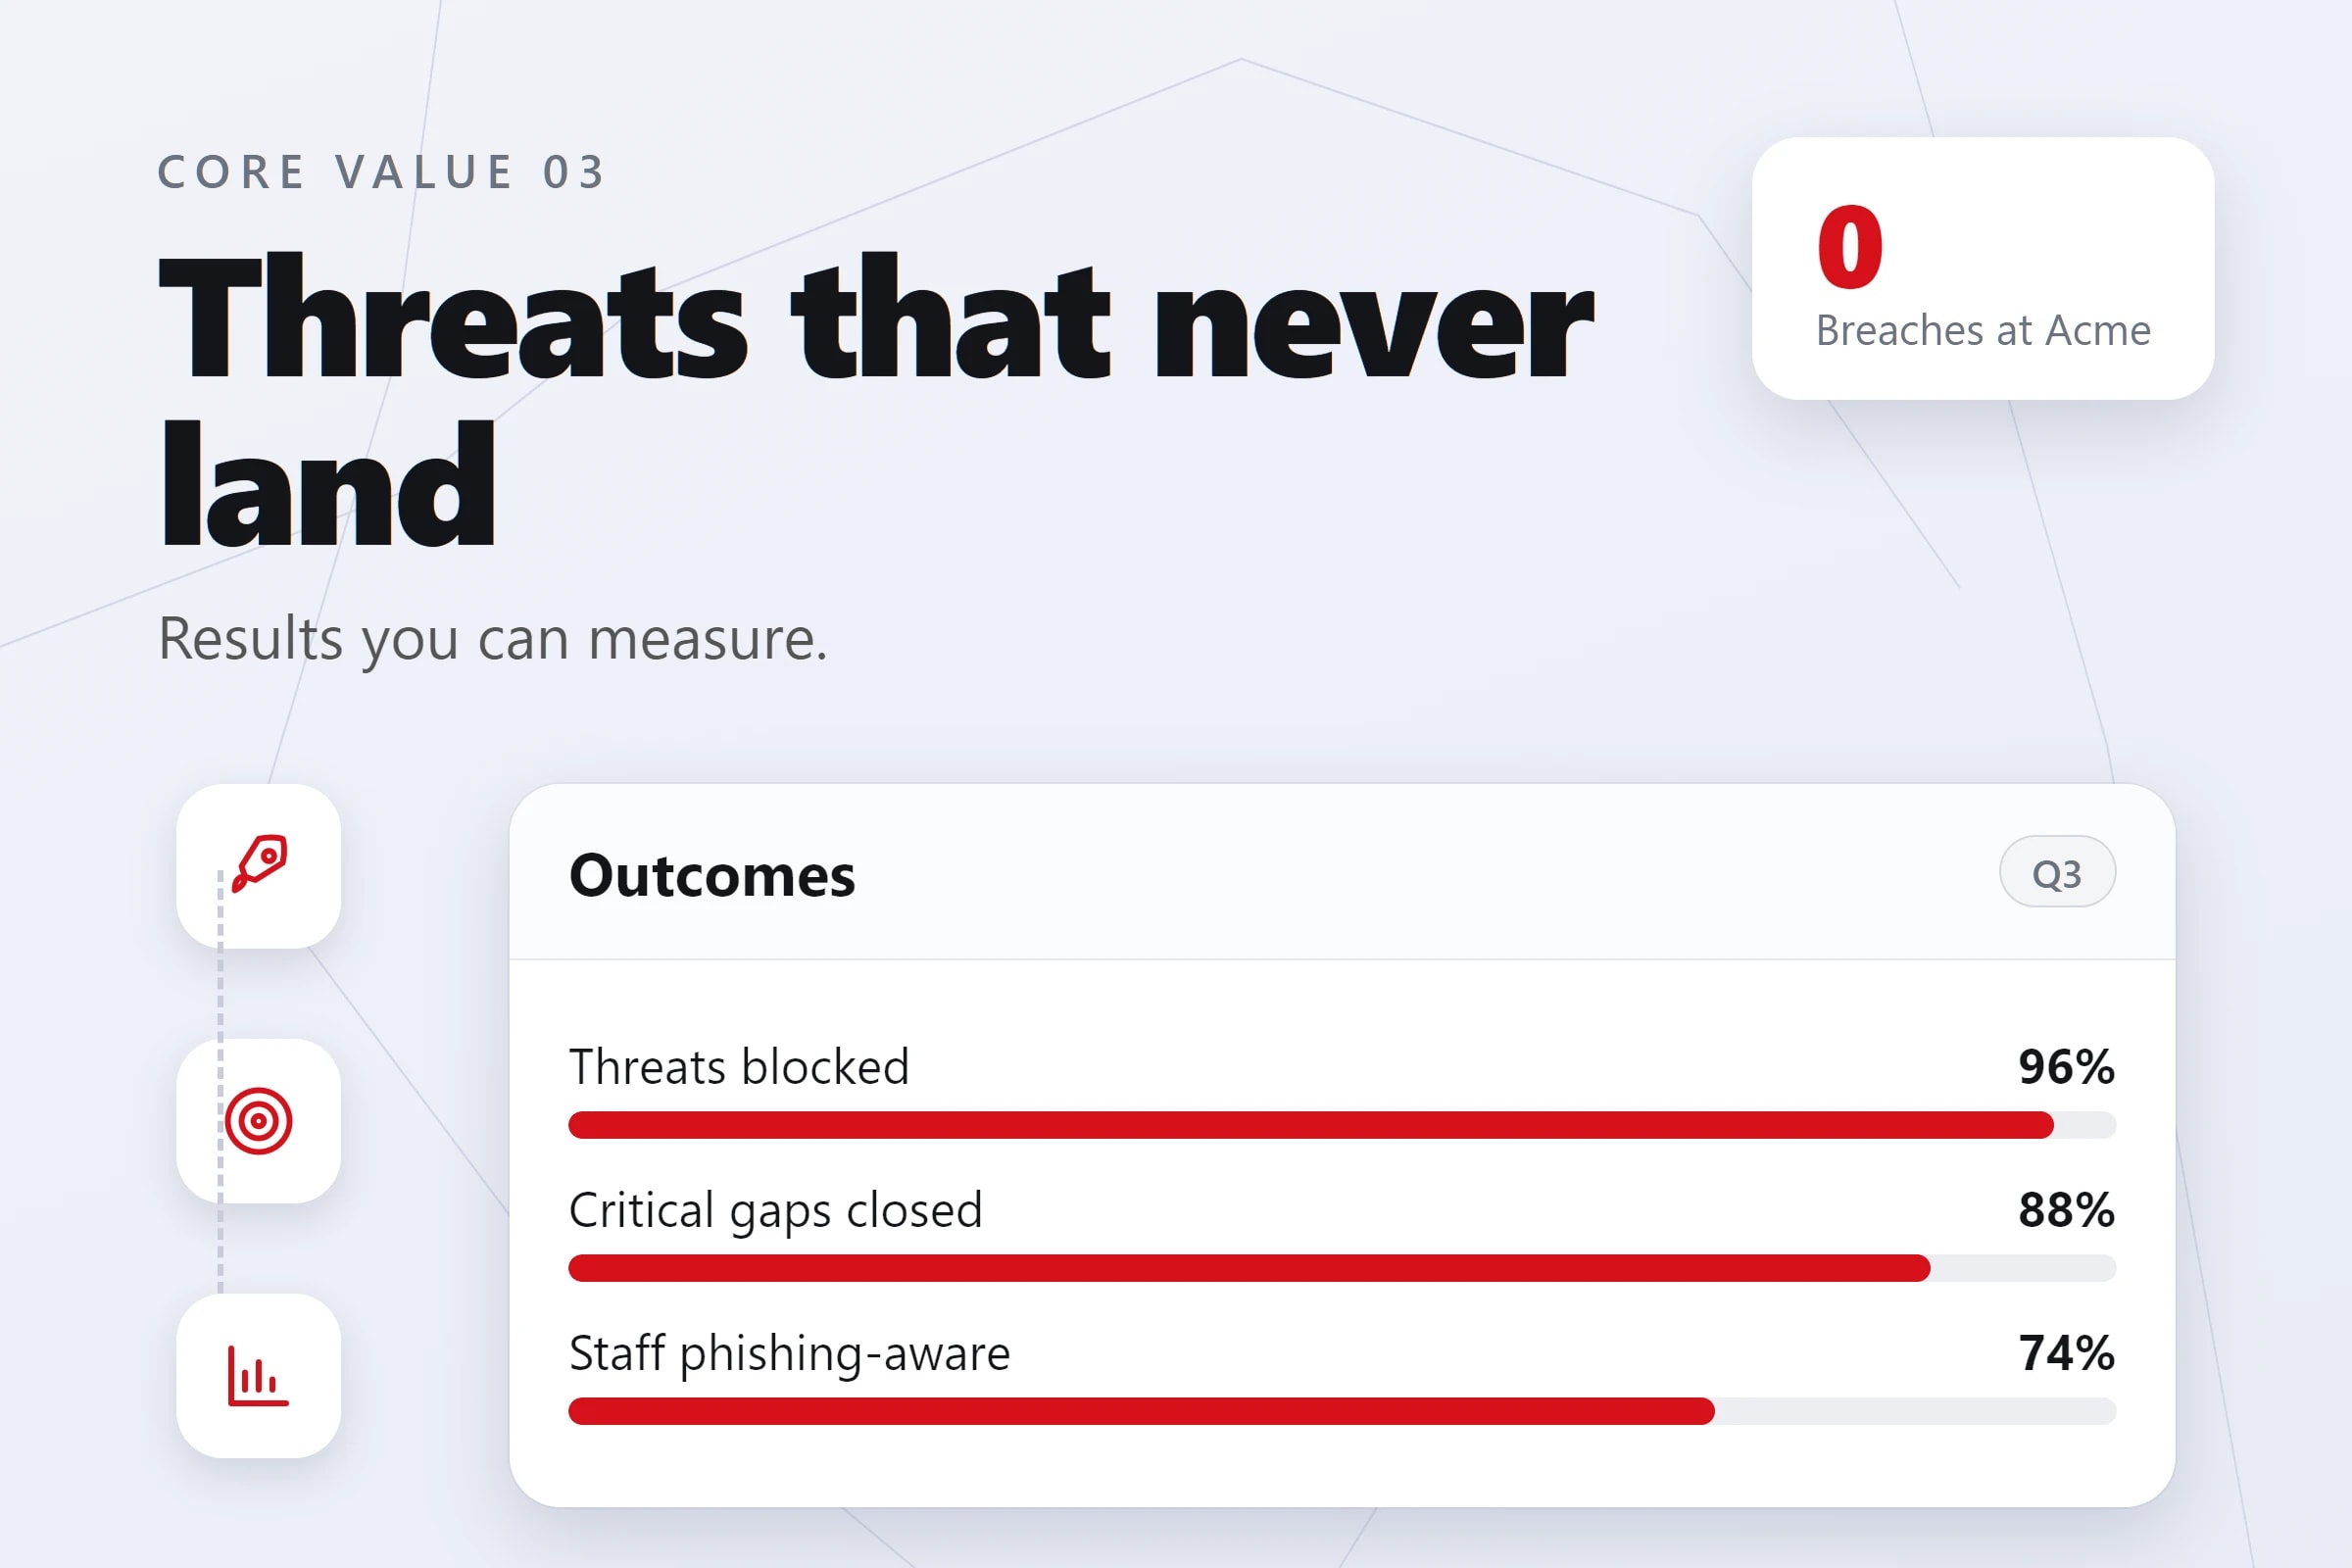
Security measured by the threats that never land.
Stop phishing, ransomware and AI-driven attacks before they start.
End-to-end encryption and real-time monitoring across every endpoint.
Hybrid AI + human teams neutralize threats and cut downtime.
Audit-ready: ISO/IEC 27001:2022 readiness, DPIA and RoPA support, and regulator audit support.
Plug into your existing stack without disrupting operations.
From startup to enterprise, we grow with you.
Agree objectives, scope and rules of engagement, and map your current posture.
Run the agreed testing and assessments, and analyse every finding in context.
Risk-rated findings with clear, prioritised remediation guidance.
Support your team through the fixes and verify them once they are in place.
0
holders
0
holders
27701 and 42001 also held
0
holders
0
holder
Mossé MPT / MRT

0
holder
0
holder
In progress

0
holder
