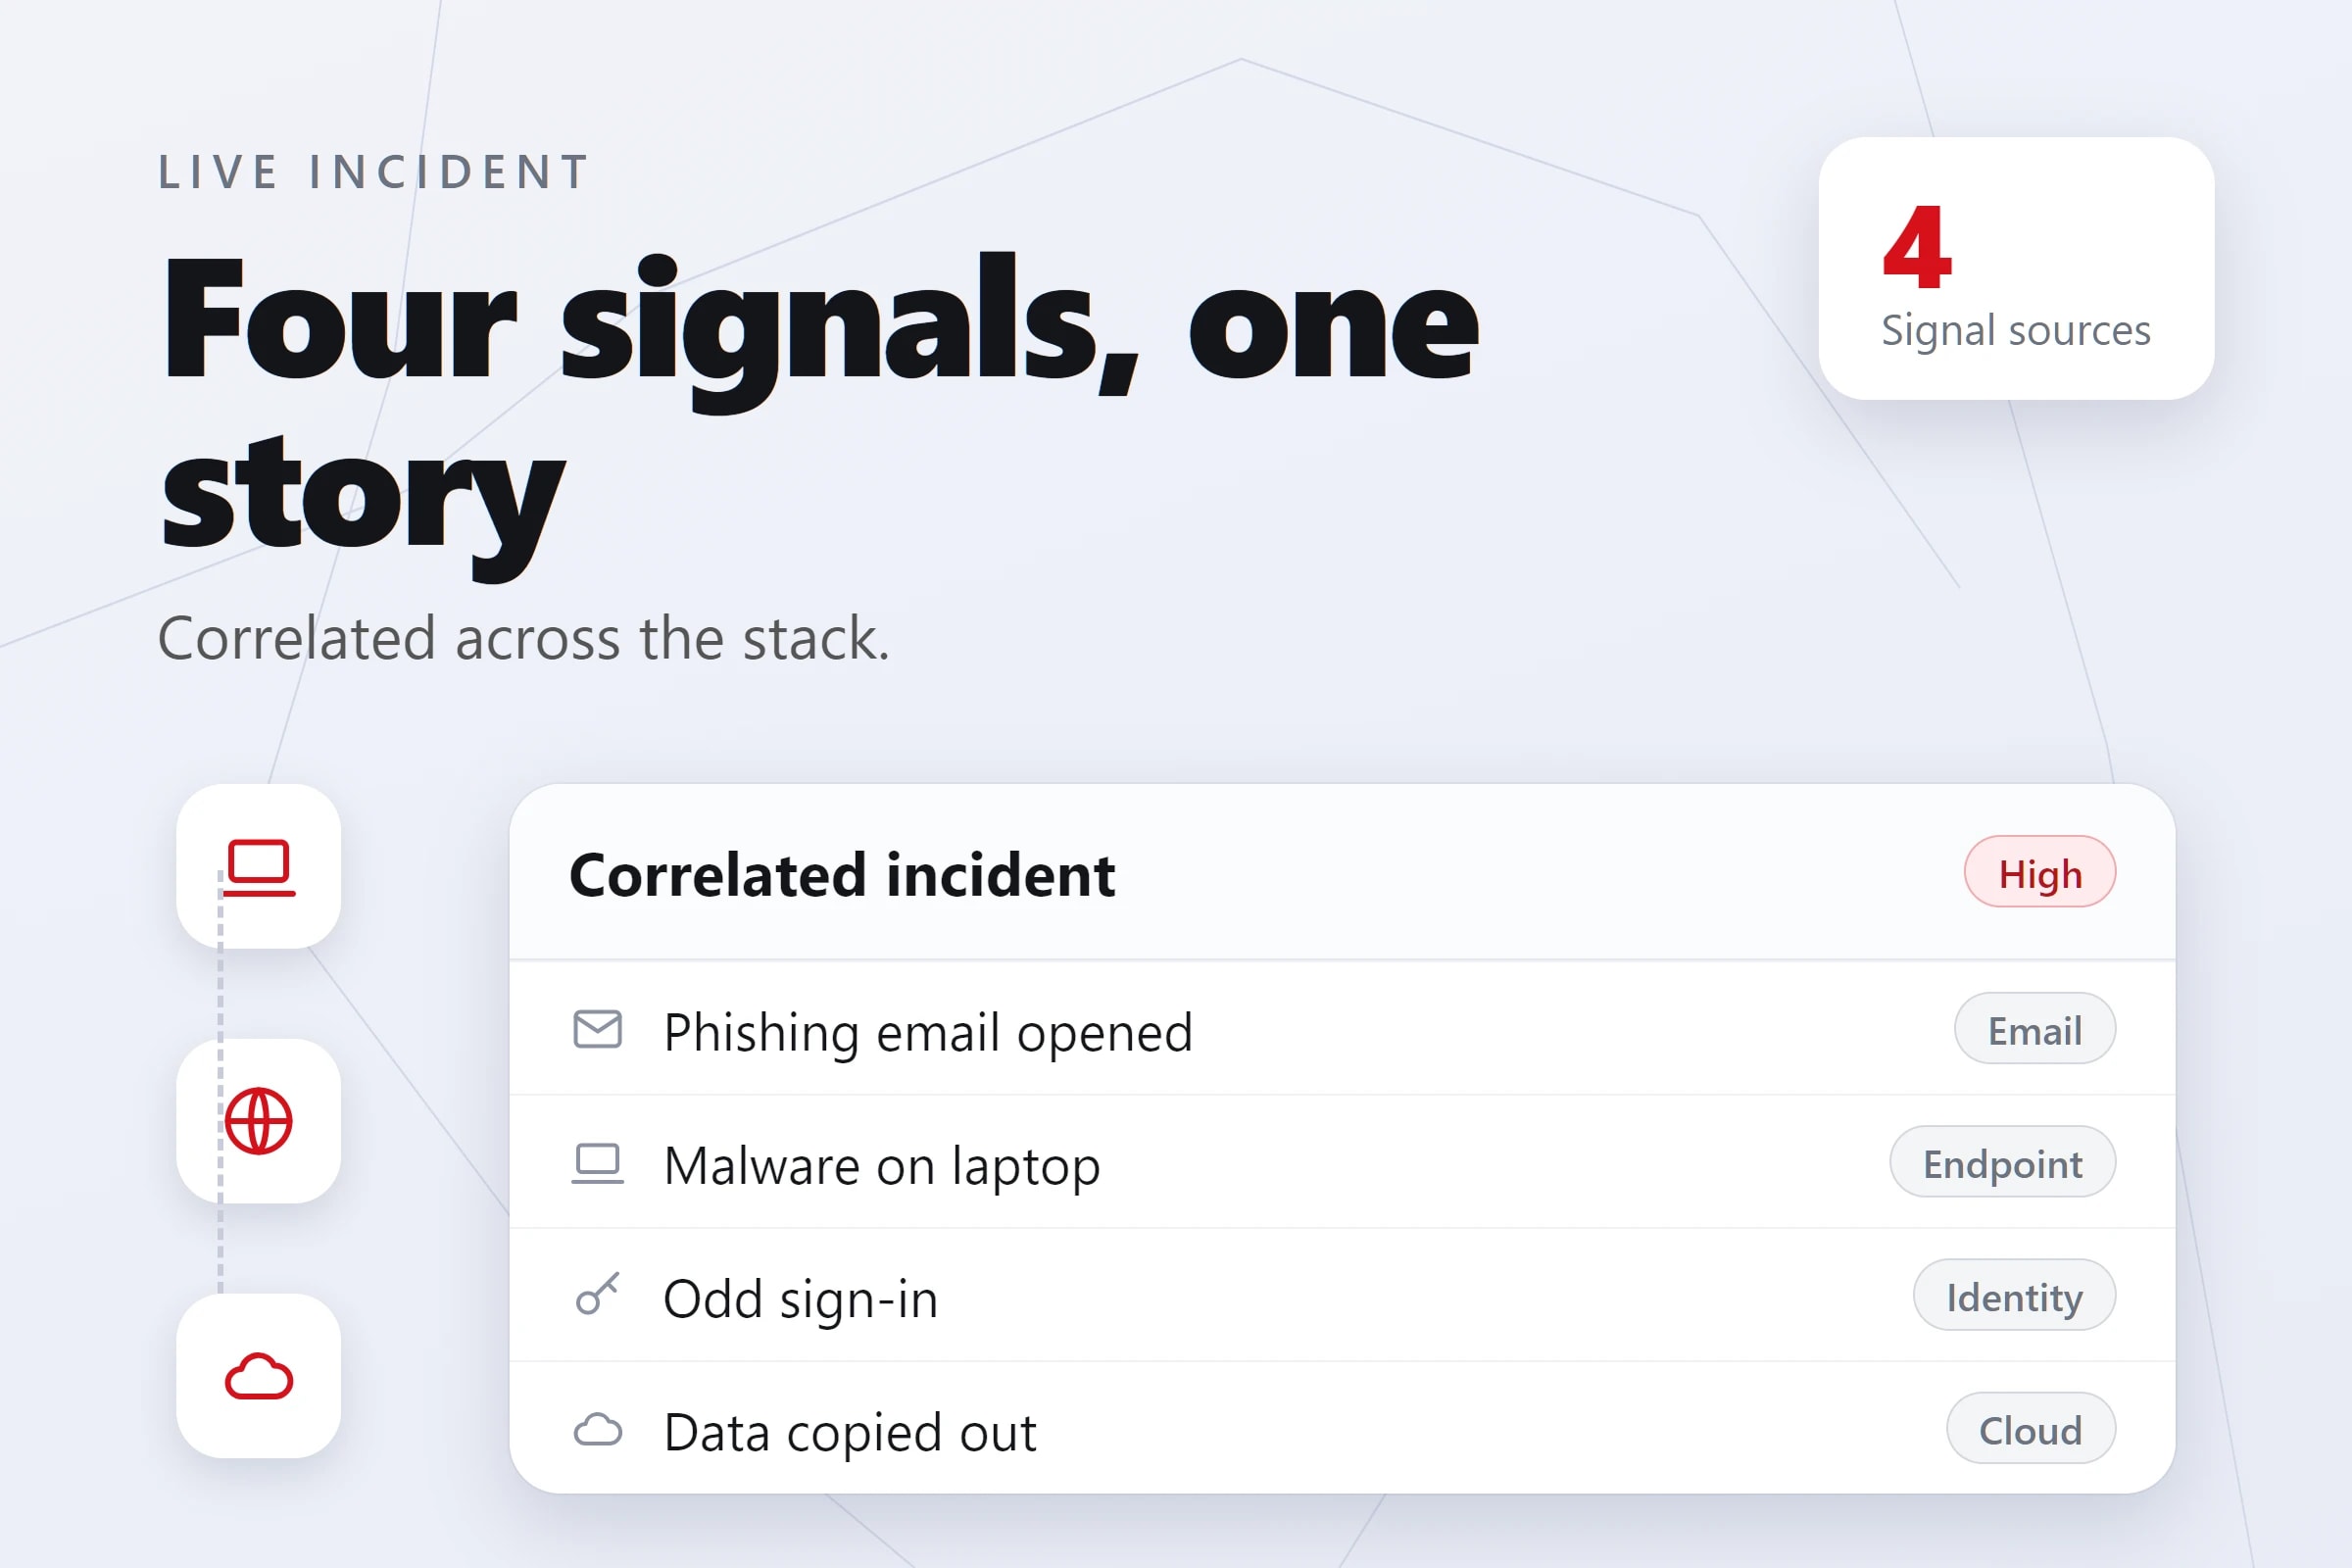
Most organizations run several security tools, each watching one part of the environment. Attackers rarely stay in one place: an intrusion might start with a phishing email, move to an endpoint and then abuse an identity to reach cloud services. Viewed tool by tool, each step can look minor.
Extended Detection and Response (XDR) brings signals from endpoints, networks, cloud services and identity systems into a single view. Automated correlation connects related events across those sources and prioritizes the alerts that matter, so threats that would slip past a single tool get caught.
The HeptaSec XDR platform covers endpoint detection and response on Windows, macOS and Linux, network traffic monitoring and anomaly detection, and cloud and identity threat detection. For organizations without an in-house SOC, optional 24/7 managed monitoring (SOC-as-a-Service) adds analysts who watch and respond around the clock.