A penetration test report is written for two audiences. The executive summary explains in plain language what was tested, what was found and what it means for the business. The technical findings give your engineers what they need to reproduce and fix each issue.
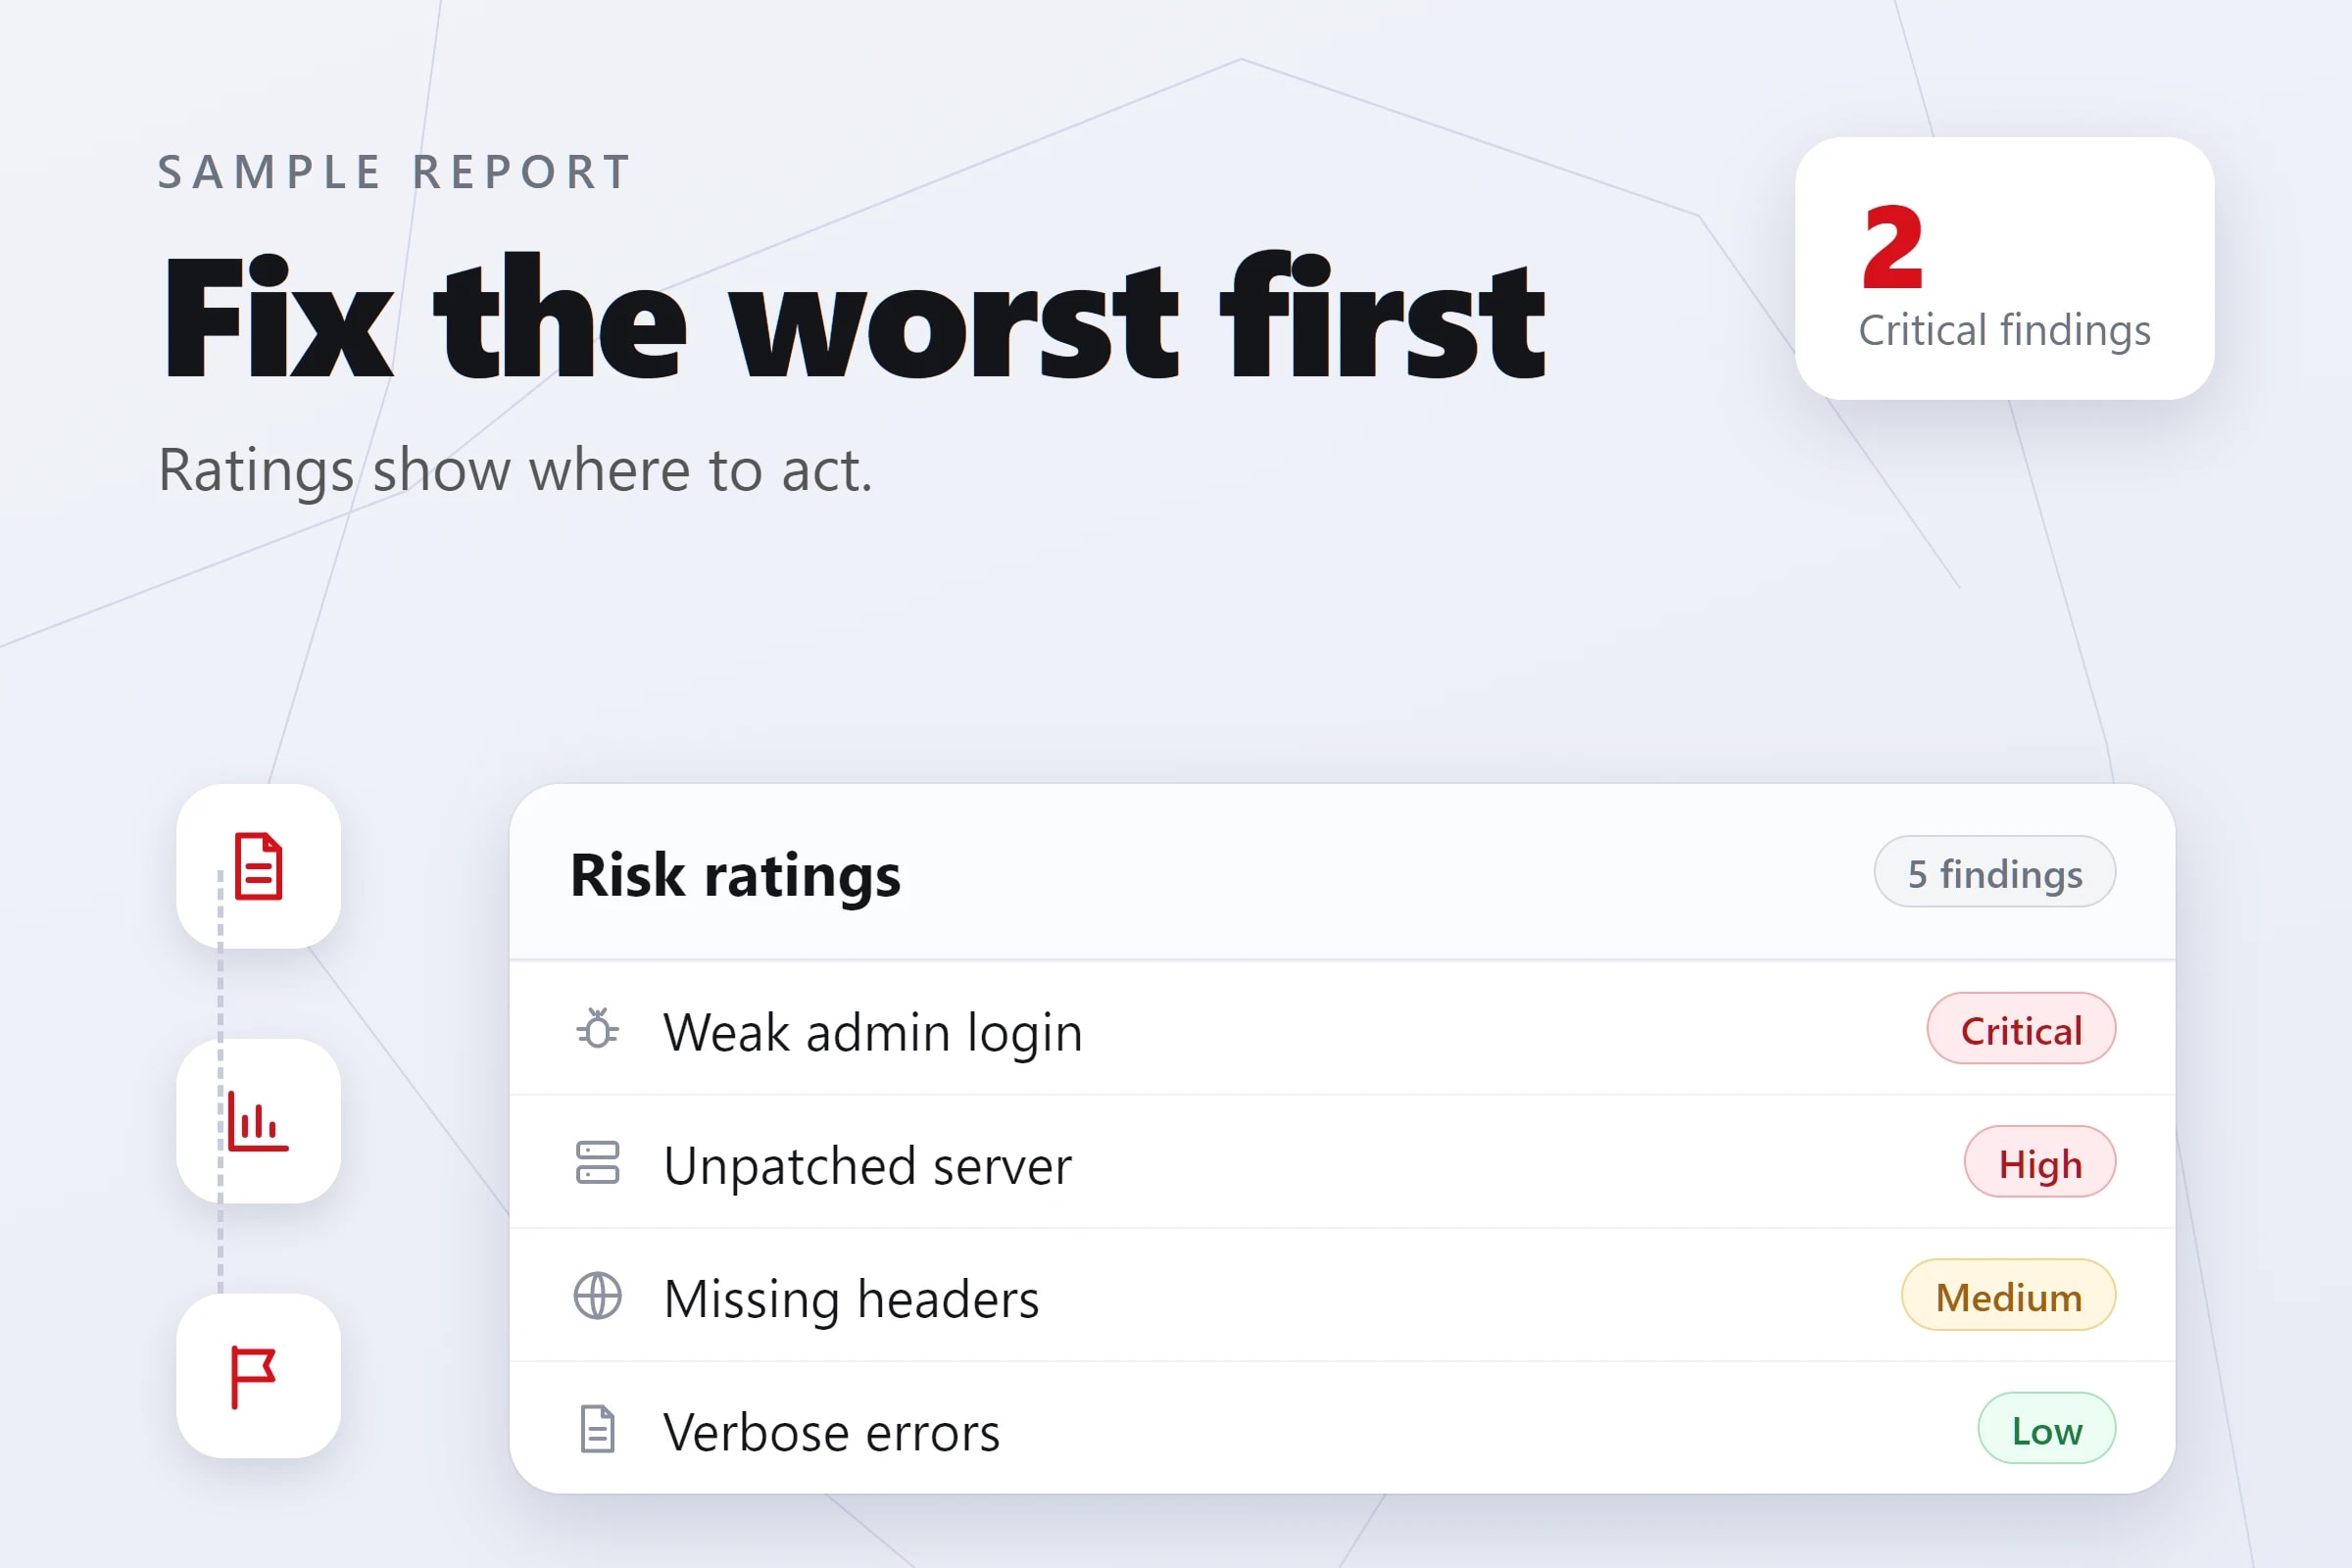
Start with the risk ratings. Each finding is rated by likelihood and business impact, so the ratings tell you where to act first. Proof-of-concept evidence shows that an issue is real and exploitable rather than theoretical, which helps your team prioritize with confidence.
Then turn to the remediation roadmap. It orders the fixes so the most important risks are handled first, and gives you a plan you can track. Once the Critical and High findings are fixed, a retest confirms the fixes work and closes them out.