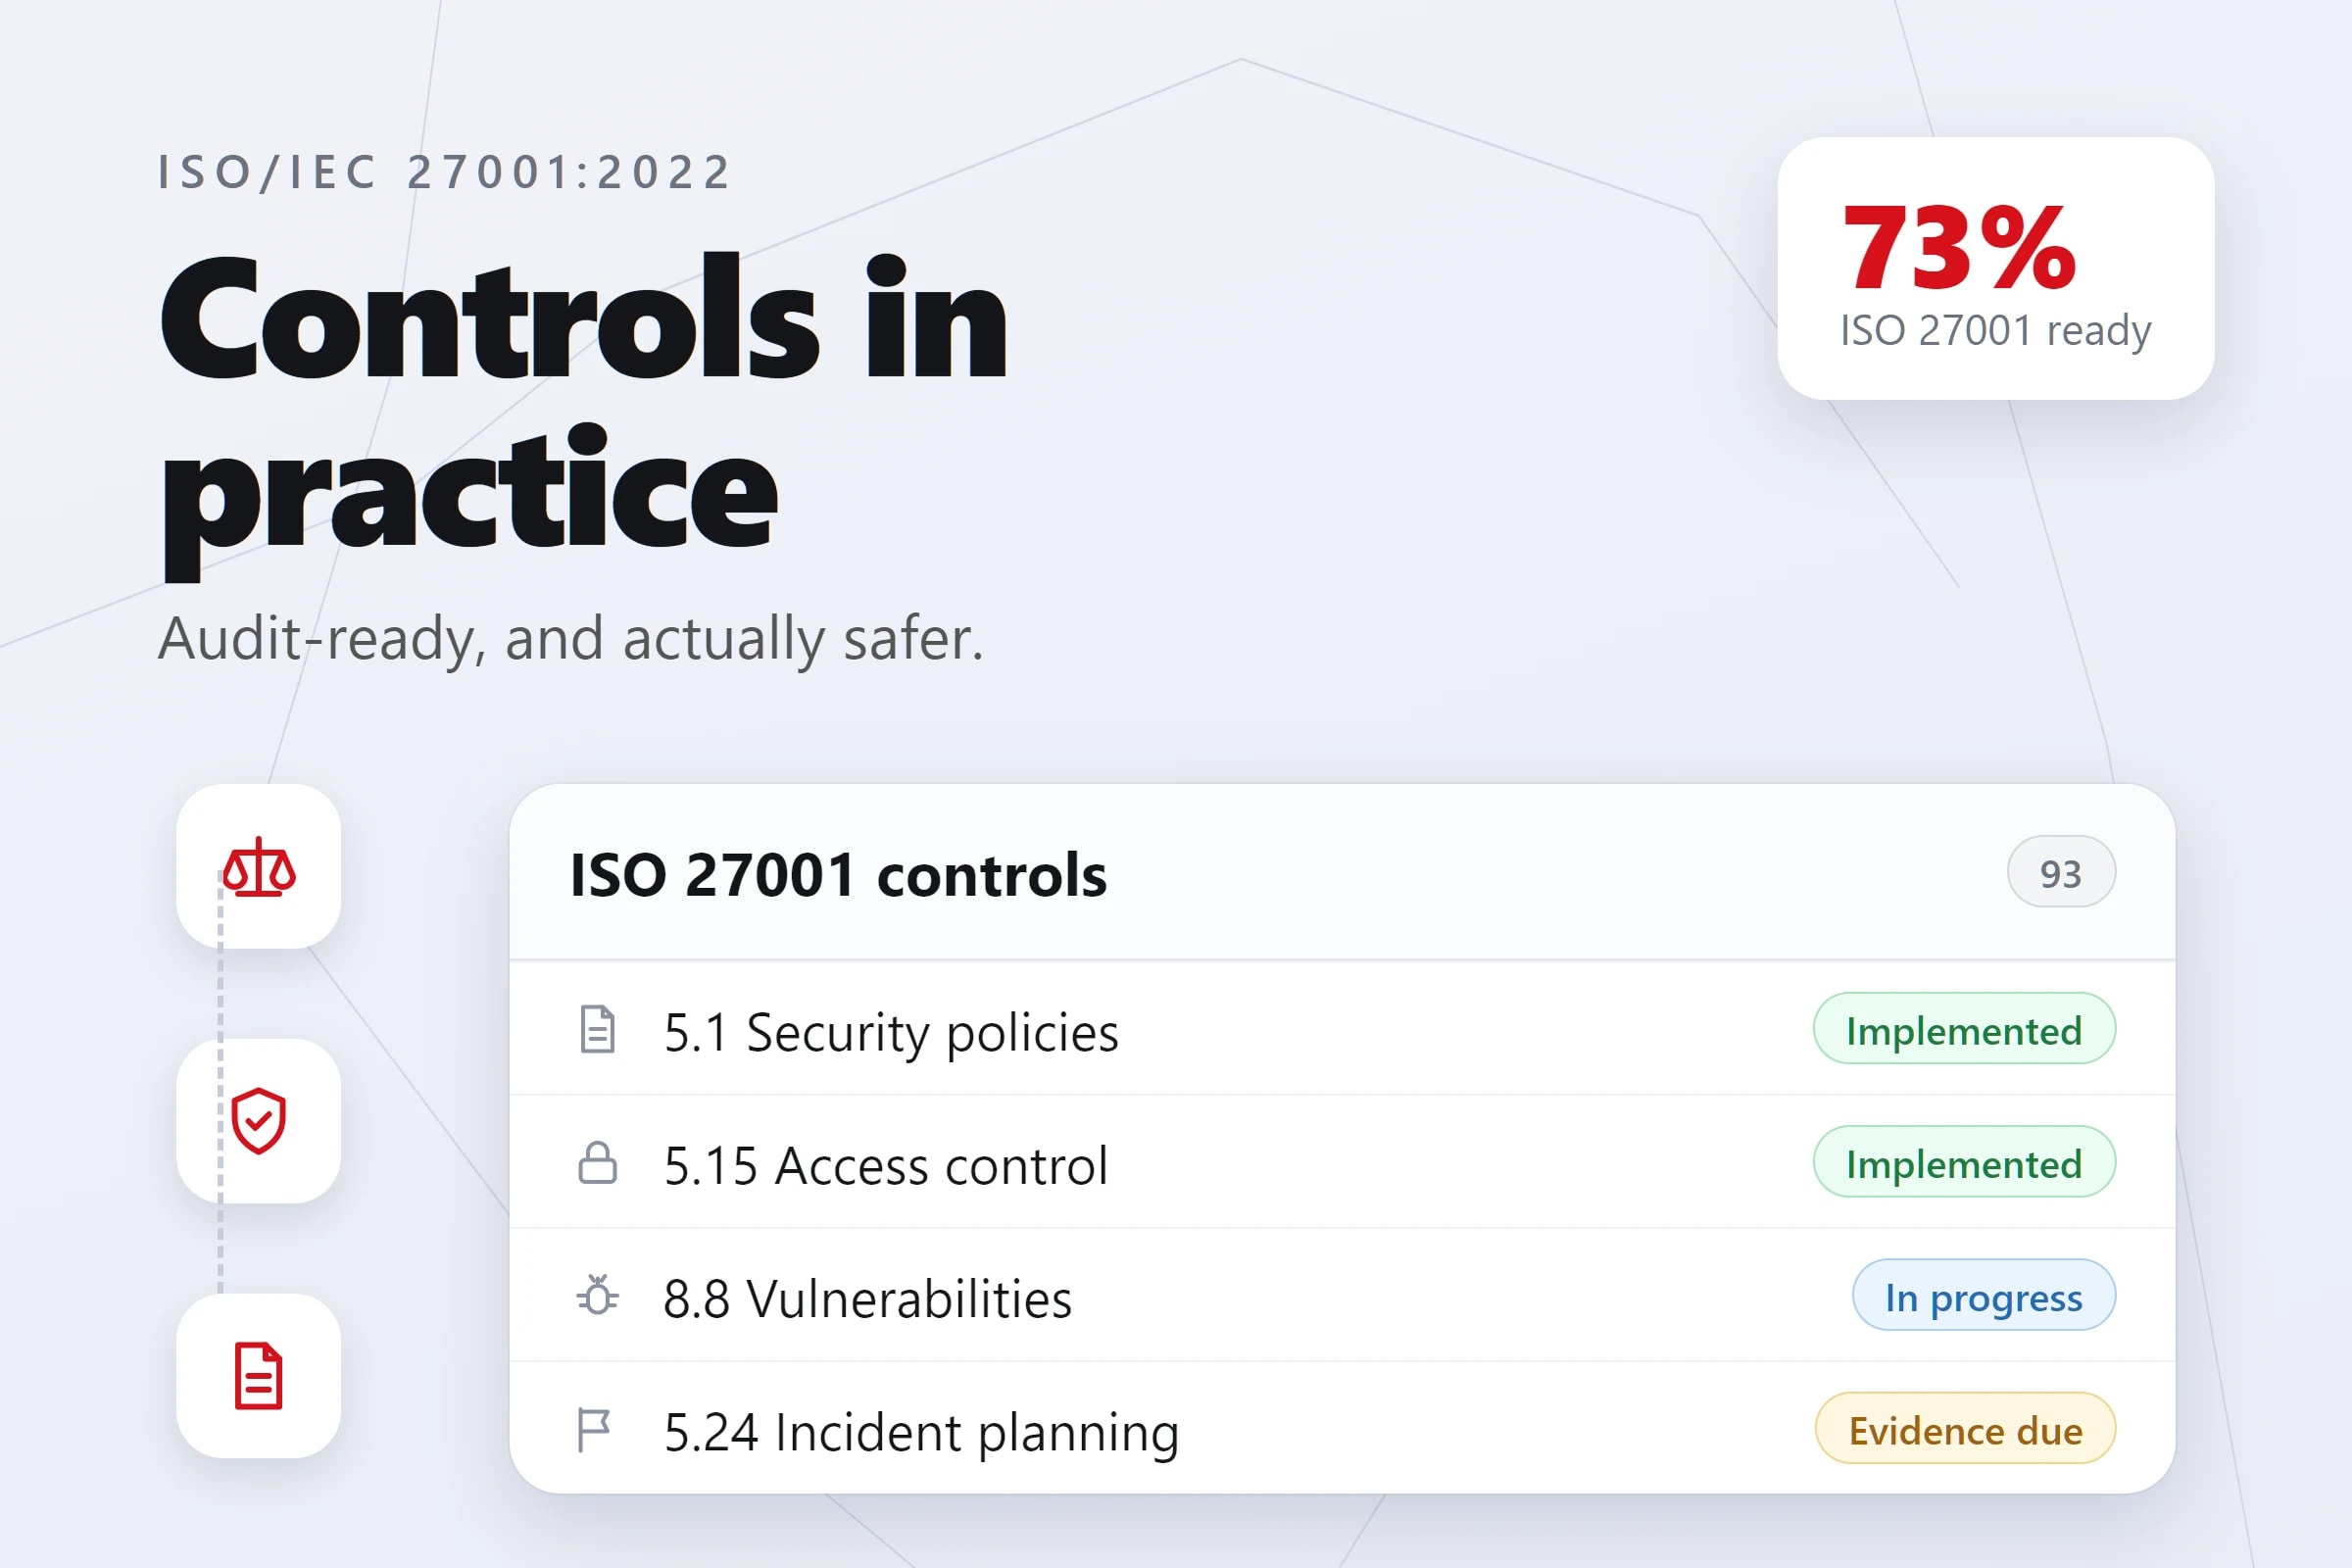
Compliance and security are not the same thing, but they should reinforce each other. An organization can pass an audit and still be exposed, or be well defended without the documentation an auditor expects. The goal is a program where each strengthens the other.
ISO/IEC 27001:2022 gives that program its structure. A gap assessment shows where you stand against the standard, and risk assessment and treatment planning decide which controls matter most for your business. The Statement of Applicability records which controls apply and why, and the information security management system (ISMS) keeps it all running.
The difference comes from building on real security work. When controls are informed by testing and genuine risk, preparing for Stage 1 and Stage 2 certification audits becomes a matter of showing evidence rather than producing paperwork, and the result is a program that reduces risk rather than one that only passes an audit.